CPA Advertising Fraud: Forced Clicks and Invisible Windows

At first glance, conversion-contingent advertising (cost-per-action / CPA, affiliate marketing) seems a robust way to prevent online advertising fraud. By paying partners only when a sale actually occurs, advertisers often expect to substantially eliminate fraud. After all, if commissions are only due when a user makes a purchase, what can go wrong? Unfortunately, this view is overly simplistic and, on balance, overly optimistic.

I’ve previously written at length about spyware and adware programs that watch a user’s web browsing in order to claim commission on sales that would have happened anyway. See last week’s examples of six different affiliates cheating VistaPrint through exactly this technique.

But CPA fraud does not require the use of spyware or adware on a user’s computer. To the contrary, I’ve seen plenty of CPA fraud that is entirely web based. Below I present three examples representative of this ongoing problem.

The Basic CPA Relationship

CPA advertising generally oblige an advertiser to pay a commission if three events occur:

  1. A user browses an affiliate’s web site;
  2. A user clicks a specially-coded link to a participant CPA merchant; and
  3. A user makes a purchase from that merchant.

The purchase in step 3 may occur immediately, i.e. within a single browsing session. But even if the purchase occurs shortly thereafter, e.g. a day later or even a few weeks later, a merchant will typically credit this purchase to the corresponding affiliate — on the view that the affiliate at least introduced the user to the merchant. This extended credit period is typically known as the “return-days period.”

Example 1: Couponcodesmall Forces Clicks to Drop Buy.com Cookies
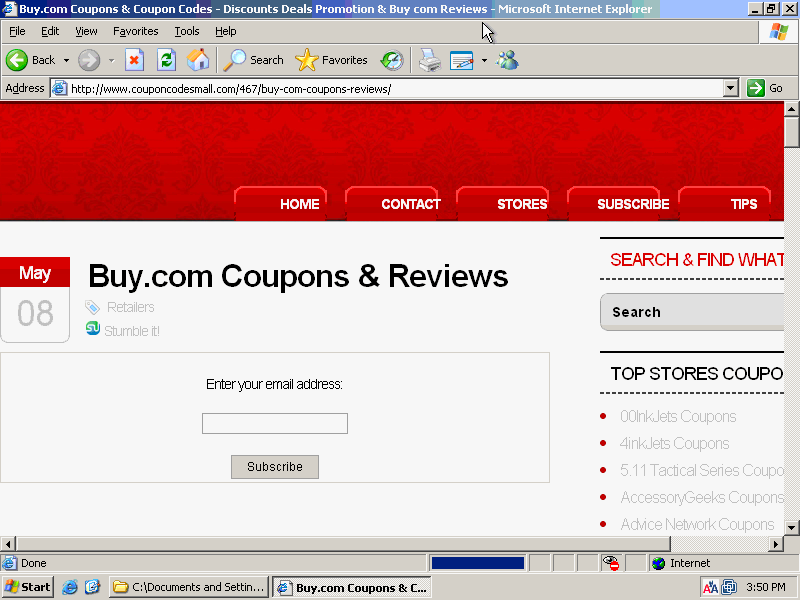
The Couponcodesmall Site - Cookie-Stuffing Invisibly The Couponcodesmall Site – Cookie-Stuffing Invisibly

Some affiliates seek to bypass the user-click requirement (event 2 above) by simulating a click on an affiliate link using JavaScript. When the user merely visits the affiliate’s site, the affiliate forces the user’s browser to load an affiliate link — thereby placing affiliate cookies on the user’s PC, and claiming an affiliate commission if the user subsequently makes a purchase from the corresponding merchant.

In 2004, I presented 36 such examples in Cookie-Stuffing Targeting Major Affiliate Merchants, But the problem is ongoing.

In testing this month, I requested a page from Couponcodesmall, a top organic result for Google searches for “buy.com coupon” (without quotes). Couponcodesmall sent more than 65KB of HTML, followed by the following IFRAME:

<iframe SRC=”http://affiliate.buy.com/gateway.aspx?adid=17662&#038;aid=10389736&#038;pid=2705091&#038;sid=&#038;sURL=http%3A//www.buy.com/” WIDTH=5 HEIGHT=5 frameborder=”0″ scrolling=”no”></iframe>

I preserved a full packet log that shows this IFRAME in context. (Edit-Find on “IFRAME” to skip to the key section.) I also preserved a screen-capture video showing the cookies created after I requested this page — confirming the IFRAME‘s effect. As the HTML instructs, the IFRAME yields no visible on-screen indication — for the IFRAME‘s 5 pixel by 5 pixel size (blue highlighting) leaves too little space for the Buy.com site to be recognized.

Buy.com’s agreement with affiliates requires that affiliates comply with Commission Junction’s Publisher Service Agreement (PSA), and PSA rule 3.a grants credit only when a user “clicks through [a] Link[] to [an] Advertiser.” This affiliate’s IFRAME-delivered forced clicks exactly violate that requirement. If a user merely views this affiliate’s page, without clicking an ad or taking any other action, then this affiliate will receive a 3% to 5% commission on any purchase the user makes from Buy.com within the next 14 days, even though the user never clicked an affiliate link as required under the PSA.

I notified the affiliate program manager for Buy.com, and I gather that Buy.com is taking appropriate action.

Similar infractions remain easy to uncover. My automated testing systems typically uncover a dozen or more violations in a day of searching. I’ve also seen all manner of advances over the popups, popunders, and IMG tags I observed in 2004. For example, I now often observe cookie-stuffing using EMBED tags, OBJECT tags, HTML entity encoding, and doubly-encoded JavaScript.

Example 2: Allebrands Banner Ads Invisibly Load Affiliate Links

Other affiliates load affiliate links and drop affiliate cookies as users merely view a banner ad. From a rogue affiliate’s perspective, this attack is more effective than the attack in Example 1, for the affiliate need not get the user to visit the affiliate’s site. Instead, merely by viewing a banner ad on a third party web page, the affiliate can drop its cookies and obtain a commission on purchases users make from the targeted merchants within the return-days period.

That is, the affiliate bypasses both the user click requirement (event 2 above) as well as the browsing requirement (event 1 above). Removing this additional requirement lets the affiliate claim commission on more users’ browsing that much more easily.

To targeted merchants, this attack is importantly worse than the attack in Example 1. In particular, through this kind of attack, a merchant receives no promotional benefit whatsoever. Under this attack, merchants pay out commission only on sales that would have happened anyway — so every commission paid is entirely wasted.

I recently observed such an attack via a banner ad running on the Yahoo RightMedia Exchange. Merely by viewing an ad from Allebrands, a user’s computer was instructed to load three affiliate links, each in a 0x0 IFRAME. Below is the relevant portion of the HTML code (formatted for brevity and clarity):

GET /iframe3? …
…
Host: ad.yieldmanager.com
…

HTTP/1.1 200 OK
Date: Mon, 29 Sep 2008 05:36:02 GMT
…

<html><body style=”margin-left: 0%; margin-right: 0%; margin-top: 0%; margin-bottom: 0%”><script type=”text/javascript”>if (window.rm_crex_data) {rm_crex_data.push(1184615);}</script>
<iframe src=”http://allebrands.com/allebrands.jpg” width=”468″
height=”60″ scrolling=”no” border=”0″ marginwidth=”0″
style=”border:none;” frameborder=”0″></iframe></body></html>

GET /allebrands.jpg HTTP/1.1
…
Host: allebrands.com
…

HTTP/1.1 200 OK
…

<a href=’http://allebrands.com’ target=’new’><img src=’images/allebrands.JPG‘ border=0></a>
<iframe src =’http://click.linksynergy.com/fs-bin/click?id=Ov83T/v4Fsg&offerid=144797.10000067&type=3&subid=0′ width =’0’height = ‘0’ boder=’0′>
<iframe src =’http://www.microsoftaffiliates.net/t.aspx?kbid=9066&p=http%3a%2f%2fcontent.microsoftaffiliates.net%2fWLToolbar.aspx%2f&m=27&cid=8′ width =’0’height = ‘0’ boder=’0′>
<iframe src =’http://send.onenetworkdirect.net/z/41/CD98773′ width =’0’height = ‘0’ boder=’0′>

The three IFRAMEs (green highlighting) load three separate affiliate links in three separate windows. Because these windows are each set to be 0 pixels wide and 0 pixels tall (blue highlighting), they are all invisible.

I preserved a full packet log of the entire HTTP sequence — showing traffic flowing from the underlying Smashits web site to Right Media to Allebrands to the target affiliate programs. (Edit-Find on “allebrands” to skip to Allebrands’ code.) I also notified the targeted merchants — McAfee, Microsoft, and Symantec. They’re taking appropriate action.
Allebrands' Decoy Ad Allebrands’ Decoy Ad

Notice Allebrands’ tricky use of the misleadingly-named /allebrands.jpg URL (yellow highlighting). In particular, Allebrands instructed Right Media to send traffic to http://allebrands.com/allebrands.jpg — a .JPG extension, so seemingly an ordinary JPEG compressed image. But despite the URL’s extension, the URL actually provided ordinary HTML — creating the A HREF, IMG, and IFRAME‘s set out above. Meanwhile, if a user happened to look at this ad, the user would see only the http://allebrands.com/images/allebrands.JPG image specified by the IMG tag (pink highlighting; image shown at right). Because the IFRAMEs are invisible (blue highlighting), the IFRAMEs yield no on-screen display whatsoever.

In my testing, Allebrands distributed its rogue banner ad via a variety of web sites. One that particularly caught my eye was Smashits, a spyware-delivered banner farm which buys widespread pop-up traffic and shows voluminous ads. Beyond Smashits’ dubious traffic origins, Smashits is also notable for its placement of ads in invisible windows: Via the two-row FRAMESET presented below, Smashits creates a 0-pixel-tall “part1” frame of /audio/empty.html, which in turn ultimately displays the Allebrands ad at issue.

<FRAMESET ROWS=”0,*” FRAMEBORDER=0 FRAMEPADDING=0 FRAMESPACING=0 BORDER=0>
  <FRAME name=part1 SRC=”http://ww.smashits.com/audio/empty.html” NORESIZE MARGINWIDTH=0 MARGINHEIGHT=0 SCROLLING=”no”>
  <FRAME name=part1a SRC=”http://ww.smashits.com/spindex_02.html” NORESIZE MARGINWIDTH=0 MARGINHEIGHT=0 SCROLLING=”yes”>
</FRAMESET>

Reviewing the packet log in the context of my prior observations of Smashits’ spyware-originating traffic, the full sequence of relationships proceeds as follows: A variety of spyware sends traffic to Smashits (often via the MyGeek / AdOn Network / Mynaagencies run-of-network ad loader), and some users may affirmatively request the Smashits site. Smashits creates a 0-pixel-tall FRAME row in which to load ads off-screen. In that frame Smashits sends traffic to Traffic Marketplace, which redirects the traffic to Theadhost, which redirects it to RightMedia Exchange, which selects an ad from Allebrands, which stuffs cookies to claim commission from the three target affiliate programs.

Who is Allebrands? Allebrands’ web site offers no contact information, and Allebrands’ Whois is equally uninformative. But Allebrands’ DNS servers reside within creativeinnovationgroup.com, and Creativeinnovationgroup’s Whois references a Simon Brown at 700 Settlement Street in Cedar Park, Texas. Google Maps confirms that this is a bona fide address — seemingly a residential unit in a development.

Example 3: Avxf Stuffing Amazon and Hostgator Cookies through Signature IMG Tags in DealOfDay Forum

In Example 1, Couponcodesmall managed to lure a user to its own web site — in part through successful search engine optimization. In Example 2, Allebrands bought traffic from Right Media. In this Example 3, affiliate rogue Avxf manages to stuff cookies using others’ traffic — without paying for that traffic.

To get traffic, Avxf places images in the footer of a message it posts to a DealOfDay.com forum discussion. The associated HTML:

Originally Posted by <strong>somerset1106</strong> …

Ditto. I am still researching some other sites that are similar. If I find out any information I will keep ya posted. …

<img src=”http://www.avxf.com/img16.jpg” border=”0″ alt=”” /><img src=”http://www.avxf.com/img17.jpg” border=”0″ alt=”” />

Avxf’s footer specified two .JPG URLs, /img16.jpg and /img17.jpg — seemingly image files based on their use of the standard .JPG file extension. But in fact these URLs redirect to affiliate programs for HostGator and Amazon:

GET /img16.jpg HTTP/1.1
…
Host: www.avxf.com

HTTP/1.1 302 Found
…
Location: http://secure.hostgator.com/cgi-bin/affiliates/clickthru.cgi?id=dsplcmnt01
…

GET /img17.jpg HTTP/1.1
…
Host: www.avxf.com

HTTP/1.1 302 Found
…
Location: http://www.amazon.com/?Fencoding=UTF8&tag=qufrho-20
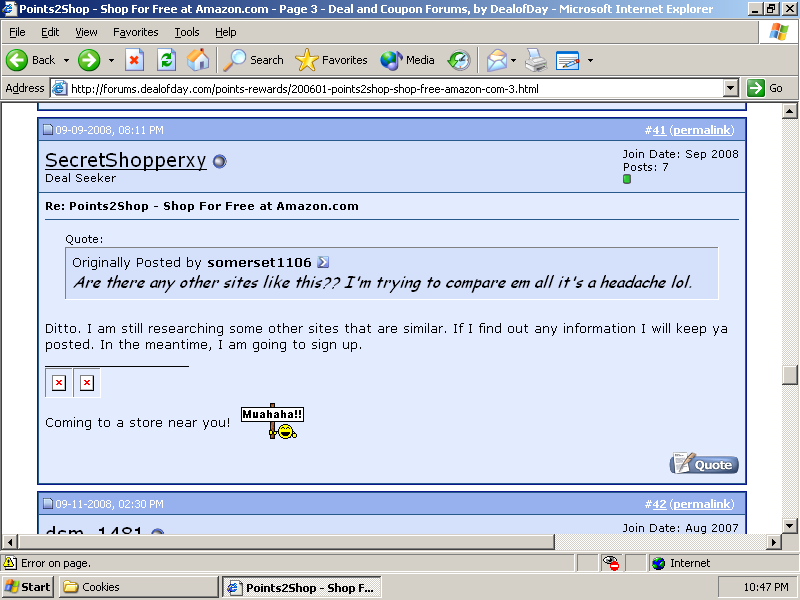
Avxf Cookie-Stuffing in DealOfDay Forum - The Resulting On-Screen Display Avxf Cookie-Stuffing:
The Resulting On-Screen Display

The resulting two pages then go on to drop affiliate cookies as usual. Thus, if a user makes a purchase at Amazon or Hostgator within their associated return-days periods, then Avxf gets paid a commission. The only on-screen indication of cookies being dropped is the two “broken image” icons shown at right — indications that something is missing, but in no way sufficient to inform a typical user (or even many advertising professionals) of what is occurring. Nonetheless, if a targeted user makes a purchase from Amazon within 24 hours of receiving Avxf’s forced click, or if a targeted user signs up with Hostgator within 30 days, then Avxf receives a commission.

I preserved a full packet log of the underlying HTML and redirects, showing Avxf’s images and redirects in context. (Edit-Find on “avxf” to skip to the code at issue.) I also preserved a screen-capture video confirming the destinations of the broken images.

Avxf’s practices violate applicable policies at Amazon and Hostgator. Amazon’s Associates program allows credit only if a customer “click[s] through” a special link (agreement 4¶1), whereas no click occurs in the example shown above. Furthermore, Amazon specifically prohibits atempts to “caus[e] any page of the Amazon Site to open in a customer’s browser other than as a result of hte customer clicking on a Special Link on [an affiliate’s] site” (agreement 4¶4). Similarly, the HostGator Affiliate Agreement prohibits the similar practice of forcing clicks through IFRAMEs (except “on pages or sites in which the other content represented on the site is related to HostGator” — an exception unavailable here, since the DealOfDay site is entirely unrelated to HostGator).

Who is Avxf? The Avxf web site offers adult content, but no mailing address on its Contact Us page. However, the site’s Whois offers a name and address: Kyle Hahn of Muncie, Indiana. Google Maps confirms the existence of the specified address, 480 W Skyway Drive.

Consequences – Winners and Losers

I see five basic consequences of these commission schemes:

  1. Fraudsters win from the bogus commission they receive, despite failing to provide merchants with a bona fide marketing benefit.
  2. Merchants pay extra commissions without getting anything in return. In particular, merchants pay commission on sales they would have made anyway. Moreover, merchants overestimate the effectiveness of their CPA marketing programs: Merchants mistakenly conclude that their CPA programs yielded sales that in fact would have happened anyway.
  3. Legitimate affiliates lose commissions that are seized by fraudsters. Whenever an ordinary affiliate was about to receive a commission, but one of these fraudsters jumps in to claim the commission instead, the first affiliate loses a commission it had fairly earned.
  4. Advertising intermediaries profit from the additional commissionable sales that purportedly occur. Affiliate networks typically charge merchants in proportion to the number (or dollar value) of commissionable sales. So every time a rogue affiliate claims commission improperly, the merchant must pay additional fees to the affiliate network.
  5. Affiliate marketing staff typically benefit, directly or indirectly, from growth in the reported size of their affiliate programs. For example, an affiliate manager might earn a bonus for rapid quarter-over-quarter growth in affiliate program size.

In principle, merchants’ losses to fraud should encourage merchants to prevent such scams. But in practice, many merchants fall victim to these attacks. Why?

For one, enforcement requires fact-intensive technical investigation — examining HTML code and packet logs to uncover infractions. The required skills have little overlap with the relationship-building and communication that otherwise drive affiliate marketing.

For some merchants and networks, mixed incentives further hinder efforts to prevent these fraudulent practices. In the short run, affiliate networks and merchants’ in-house affiliate marketing staff stand to lose from rigorous enforcement — reducing their commissionable base, reducing the size of their marketing programs, and distracting their attention from activities that more directly increase their respective short-run compensation. Thus, in the short run, both groups may perceive that they can increase their profits by deemphasizing fraud prevention.

Of course, in the long run, affiliate networks have reputations to protect. Similarly, affiliate marketing staff must consider their duties to their employers; in the long run, employers may learn about these scams and think unfavorably of marketing staff who failed to take effective action to uncover improper practices.

Large Merchants at Heightened Risk

For many cookie-stuffing attacks, large merchants are at highest risk. For example, Avxf is essentially betting that the users who read DealOfDay will subsequently go on to make purchases from Amazon. As to Amazon, that’s a safe bet, for many users buy from Amazon with remarkable regularity. But if Avxf were to target a lesser-known merchant, it would face tougher odds and lower earnings.

Thus, these random cookie-stuffing attacks (as in Examples 2 and 3) tend to target large merchants. In contrast, SEO-based attacks, as in Example 1, can prey on CPA merchants of any size.

Prevention and Response

For merchants and networks seeking to uncover and prevent these practices, I see three clear ways forward:

  • Analyze statistics already on hand . Look for unusually high click-through rates, unusually low conversion rates, blank or unexpected HTTP Referer headers, unusual HTTP User-Agent headers, long delays between clicks and sales, and other errata. But beware of affilates who manage to manipulate these statistics.
  • Provide a report / complaint page. It’s surprisingly difficult for independent affiliates, users and researchers to report fraud to many online marketers. But such reports can be extremely useful — particularly when gathered by those with a special interest in catching these scams. There’s ample evidence that affiliates enjoy reporting scams: In the ParasiteWare forum at ABestWeb, affiliates and others analyze and reveal improper marketing practices; some merchants pay bounties to anyone reporting fraud by their affiliates (1, 2).
  • Conduct hands-on testing. Browse the web looking for such scams. Run a network monitor to detect any unexpected “click” events. Or, design appropriate software to conduct such tests automatically.

Separately, merchants and networks can sensibly deter violations through tough penalties. At present, affiliates face little downside to attempting to defraud most merchants. In Deterring Online Advertising Fraud Through Optimal Payment in Arrears, I suggest a different approach — paying affiliates more slowly so that they face greater losses if they are found to be cheating. Meanwhile, some merchants have resorted to suing fraudulent affiliates. See eBay v. Digital Point Solutions (accusing affiliates of cookie stuffing through invisible code claiming unearned commissions — like the examples above) and Lands’ End v. Remy (accusing affiliates of typosquatting on Lands’ End trademarks and redirecting to Lands’ End’s LinkShare affiliate links).

More generally, merchants ought not assume infallibilityof their online marketing schemes. Certainly CPA marketing programs avoid some of the more obvious problems of pay-per-click marketing (e.g. click fraud), but CPA campaigns remain vulnerable to other kinds of abuse. Shrewd merchants should anticipate what can go wrong, and design and audit accordingly.
Auditing Spyware Advertising Fraud: Wasted Spending at VistaPrint

“VistaPrint is disciplined in operation … [VistaPrint’s] marketing [uses] highly analytically driven fact-based decision-making … [W]e manage those [marketing partners] tightly.”

– VistaPrint CEO Robert Keane in a January 2008 earnings call

For more than four years, I’ve been monitoring online advertising — alerting advertisers, ad networks, and the general public when ad spending finds its way to spyware vendors and when advertisers are getting cheated. (Examples: 1, 2, 3, 4, 5) Every day, my Automatic Spyware Tester browses the web on multiple spyware-infected PCs, watching for spyware-delivered advertising and recording its observations in videos and packet logs.

Although VistaPrint’s Robert Keane claims to effectively oversee VistaPrint’s marketing practices, I emphatically disagree. To the contrary, I’ve seen ample evidence of VistaPrint promoted by spyware and adware programs that sneak onto users’ computers without consent (including through security exploits) and through ruse and deception. In many instances, including as detailed in the examples that follow, the corresponding affiliates trick marketing analytics — claiming commission on sales that would have happened anyway, and thereby overstating the true effectiveness of their marketing efforts.

When VistaPrint is cheated by rogue marketing partners, the costs fall in the first instance to VistaPrint shareholders. Every dollar wasted on worthless advertising leaves that much less for corporate profits, and VistaPrint’s advertising budget is already strikingly large: In 2008, VistaPrint marketing consumed 31.9% of revenue (more than $125 million) while profits were just 9.9% ($39.7 million). Meanwhile, fraud against VistaPrint also harms the general public: Consumers suffer unwanted installations of spyware programs funded, in part, by theft from VistaPrint.

The following table summarizes my recent observations of fraud against VistaPrint:

Ad network Example incident Rogue VistaPrint incidents observed
August – September 2008 January – July 2008
Number of affiliates Number of dates Number of observations Number of observations
Lynxtrack Vomba, Hydra Network Affiliate 19934 6 13 18 32
Clickbooth Vomba, Clickbooth Affiliate 14941
WhenU, MediaTraffic, Iadsdirect, Clickbooth Affiliate 7781
5 13 14 14
CPA Builder (including traffic from Revenue Gateway, from OptInRealBig / CPAEmpire, and from XY7) Zango, Revenue Gateway Affiliate 12489, CPA Empire, CPA Builder 2 8 9 21
CX Digital Media (Incentaclick) Vomba, Weclub, CX Digital Media Affiliate 13736 2 2 2 18
Performics (Google) Deluxe Communications, Smartyseek, Performics 1 5 5 5
direct relationships & other networks
not yet tabulated in full – some examples on file

During August-September 2008, my AutoTester repeatedly observed VistaPrint facing rogue traffic coming from five different ad networks. In the sections that follow, this piece presents an example of fraud by an affiliate from each of the specified networks. But I’ve seen plenty more. My AutoTester has been running for more than a year — preserving tens of thousands of records of online advertising fraud, including 133 other spyware incidents arising out of traffic to VistaPrint. These many incidents confirm the breadth of improper practices by VistaPrint’s marketing partners.

Example 1: Vomba, Hydra Network Affiliate 19934 Claiming Commission on VistaPrint’s Organic/Type-In Traffic

Vomba, Lynxtrack Affiliate 19334 Targeting VistaPrintVomba, Hydra Network Affiliate 19334 Targeting VistaPrint

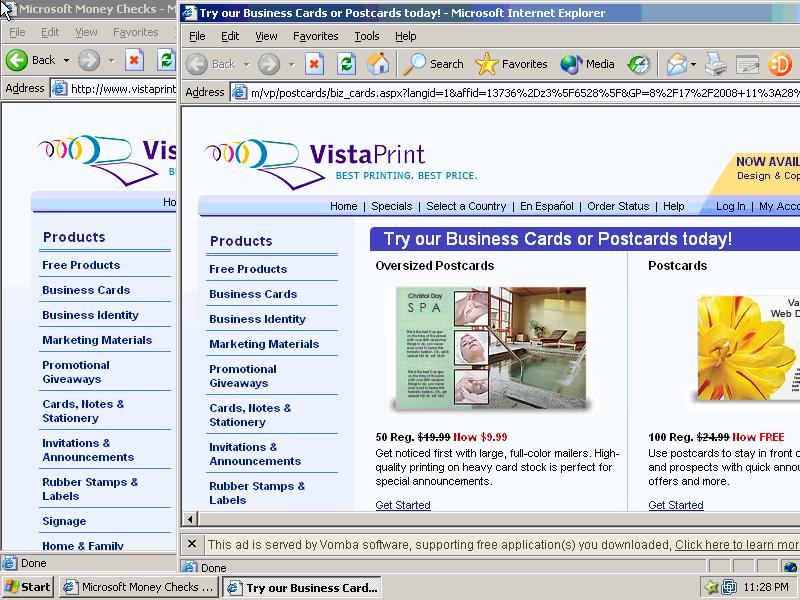
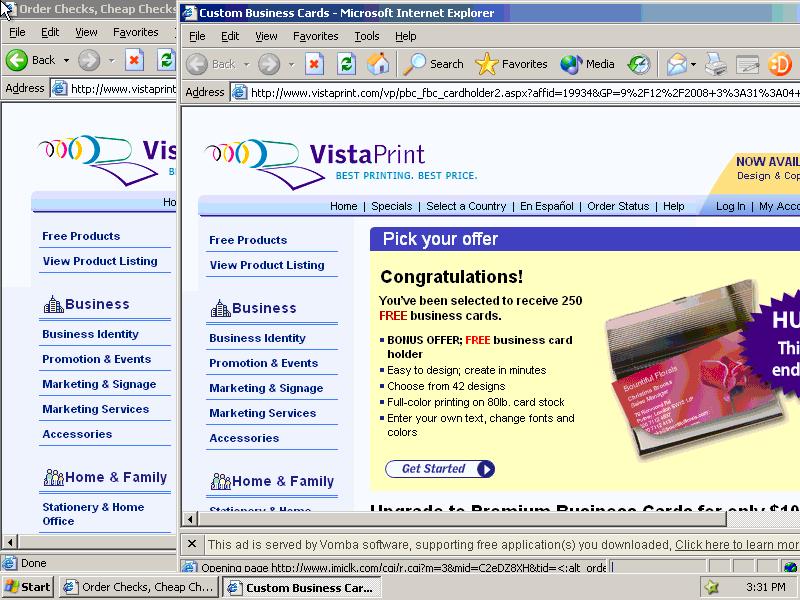
In testing on September 12, my AutoTester browsed VistaPrint’s site on a computer with Vomba (from Integrated Search Technologies, makers of Slotchbar, XXXtoolbar, WhenU, AdVantage, and more). Vomba popped open a window that sent traffic to Hydra Network (LynxTrack) (affiliate 19934), and Hydra Network in turn forwarded the traffic back to VistaPrint. The result was the screen shown at right — the original VistaPrint window at left/back, with a new popup at front/right.

Crucially, both web browser windows share a single set of cookies. Whether the user buys from the original VistaPrint window or from the popup, cookies tell VistaPrint that this Hydra Network affiliate caused the sale. So VistaPrint will pay this affiliate a commission — even though, in fact, the affiliate did nothing whatsoever to facilitate the sale. I call this tactic “self-targeting” — reflecting that Vomba covers VistaPrint with its own ad. All of the examples presented on this page entail spyware/adware performing this kind of self-targeting attack.

My AutoTester preserved a video of this incident and a packet log of the underlying network traffic.

My AutoTester observed this same affiliate using the same method on three different dates in August-September 2008. My AutoTester also observed five other Hydra Network affiliates similarly defrauding VistaPrint. All told, in August-September, my AutoTester observed 18 such incidents on 13 distinct dates.

My AutoTester’s records indicate that Hydra Network receives substantial spyware-originating traffic. Looking back to June 2007, across all my AutoTester’s browsing, my AutoTester has seen a remarkable 1,287 instances of spyware sending traffic to/through Hydra Network.

Example 2: Vomba, Clickbooth Affiliate 14941 Claiming Commission on VistaPrint’s Organic/Type-In Traffic

In testing on September 12, my AutoTester browsed VistaPrint’s site, again on a computer with Vomba. Vomba popped open a window that sent traffic to Clickbooth (affiliate 14941), and Clickbooth in turn forwarded the traffic back to VistaPrint.

Because both web browser windows share a single set of cookies, this Clickbooth affiliate gets paid a commission whether the user buys from the original VistaPrint window or from the popup. This commission gets paid even though, in fact, the affiliate did nothing whatsoever to facilitate the sale.

My AutoTester preserved a video of this incident and a packet log of the underlying network traffic.

My AutoTester observed this same affiliate using the same tactics on eight different dates in August-September 2008. My AutoTester also observed three other Clickbooth affiliates similarly defrauding VistaPrint. All told, my AutoTester observed 13 such incidents on 12 distinct dates.

My AutoTester’s records indicate that Clickbooth receives substantial spyware-originating traffic. Looking back to June 2007, across all my AutoTester’s browsing, my AutoTester has seen 917 instances of spyware sending traffic to/through Clickbooth.

Example 3: WhenU, MediaTraffic, Iadsdirect, Clickbooth Affiliate 7781 Claiming Commission on VistaPrint’s Organic/Type-In Traffic

In manual testing on September 28, I browsed VistaPrint’s on a computer with WhenU. WhenU opened a popunder that flashed briefly on screen (video at 0:15) but then forced itself to an off-screen location where I could not see it even if I minimize other windows. (See video at 0:24 to 0:30, when I attempted to find the popunder.) By manually right-clicking and choosing “maximize,” I managed to make the popunder visible — confirming that it loaded VistaPrint and noting the affiliate ID number.

Packet log analysis reveals that traffic flowed from WhenU to MediaTraffic (a pay-per-view advertising marketplace also operated by Integrated Search Technologies) to Iadsdirect to Clickbooth (affiliate 7781) to VistaPrint.

As in prior examples, both windows share a single set of cookies. Thus, the WhenU popunder causes the corresponding affiliate to receive a commission if the user makes a purchase — even though the affiliate did nothing to encourage or facilitate a purchase.

I preserved a video of this incident and a packet log of the underlying network traffic.

This advertising fraud by WhenU is particularly notable because WhenU previously claimed to have reformed all unsavory practices. (See e.g. “WhenU CEO Bill Day Cleans House.”) Moreover, WhenU previously touted a TRUSTe Trusted Download certification, and TRUSTe specifically prohibits Trusted Download programs from defrauding advertisers. (See Certification Agreement, Schedule A (“Program Requirements”), provision 14.k.) That said, WhenU has silently left the Trusted Download whitelist. Furthermore, in separate testing of WhenU software, I have recently seen repeated self-targeting fraud improperly claiming commissions from a variety of advertisers.

Example 4: Zango, Revenue Gateway Affiliate 12489, CPA Empire, CPA Builder Claiming Commission on VistaPrint’s Organic/Type-In Traffic

VistaPrint
money viewers
   CPA Builder    
money viewers
   CPA Empire    
money viewers
   Revenue Gateway    
money viewers
Zango

The Money Trail and Traffic Flow

In testing on September 21, my AutoTester browsed VistaPrint’s site on a computer with Zango. Zango popped open a window that sent traffic to Revenue Gateway (affiliate 12489), which redirected to CPA Empire (formerly OptInRealBig), which redirected to CPA Builder, which in turn forwarded the traffic back to VistaPrint.

The chain of intermediaries adds additional complexity to the relationships. But traffic flows in a continuous forward path: From Zango to Revenue Gateway to CPA Empire to CPA Builder and finally back to VistaPrint. Conversely, revenue flows in the opposite direction: From VistaPrint to CPA Builder to CPA Empire to Revenue Gateway to Revenue Gateway affiliate 13425 to Zango. The diagram at right summarizes the flows of traffic and money.

My AutoTester preserved a video of this incident and a packet log of the underlying network traffic.

During August-September 2008, my AutoTester also observed other incidents wherein spyware waited for a user to browse the VistaPrint site, then sent the user back to VistaPrint via CPA Builder. Beyond this Zango / Revenue Gateway / CPA Empire example, I also observed incidents wherein CPA Empire’s relationship with XY7 was the source of the tainted traffic. All told, my AutoTester has preserved more than 600 incidents of spyware sending traffic to/through CPA Empire, as well as at least 24 incidents of spyware sending traffic to/through Revenue Gateway (though I have reason to believe that some Revenue Gateway incidents were not preserved).

Example 5: 8/17/08 – Vomba, Weclub, CX Digital Media (Incentaclick) Affiliate 13736 Claiming Commission on VistaPrint’s Organic/Type-In Traffic

Vomba, Weclub, CX Digital Media Affiliate 13736 Targeting VistaPrint Vomba, Weclub, CX Digital Media Affiliate 13736 Targeting VistaPrint

In testing on August 17, my AutoTester browsed VistaPrint’s site on a computer with Vomba. Vomba popped open a window that sent traffic to Weclub, which immediately redirected to CX Digital Media (Incentaclick), which in turn forwarded the traffic back to VistaPrint.

See the screenshot at right. My AutoTester preserved a video of this incident and a packet log of the underlying network traffic.

During August-September 2008, my AutoTester also observed another CX Digital Media affiliate using spyware to claim commission on VistaPrint’s organic traffic. All told, my AutoTester has preserved more than 200 different incidents of spyware sending traffic to/through CX Digital Media.

Example 6: Deluxe Communications, Smartyseek, Performics Claiming Commission on VistaPrint’s Organic/Type-In Traffic

In testing on September 14, my AutoTester browsed VistaPrint’s site on a computer Deluxe Communications (which I have repeatedly observed installed through security exploits and otherwise without user consent). Deluxe Communication popped open a window that sent traffic to Smartyseek, which immediately redirected to Performics, then back to VistaPrint.

In typical Deluxe Communications fashion, the popup window entirely covered the window the user had been browsing. But because both windows showed VistaPrint, some users might not notice.
My AutoTester preserved a video of this incident and a packet log of the underlying network traffic.

My AutoTester observed this same affiliate using the same tactics on five different dates in August-September 2008, and my AutoTester also observed Performics traffic during VistaPrint browsing on five other (prior) occasions.

Responsibility and Causation

It’s easy to present VistaPrint as perpetrator: VistaPrint fails to adequately oversee its marketing partners. As a result, VistaPrint’s advertising spending helps fund spyware and adware programs that sneak onto users’ PCs, with serious harms to performance, reliability, and privacy.

But I also see an important sense in which VistaPrint is a victim: VistaPrint’s marketing partners are defrauding VistaPrint by claiming commissions on sales they actually did nothing to cause. Such commissions are entirely wasted, yielding no bona fide marketing benefit to VistaPrint.
By all indications, VistaPrint faces significant difficulties in supervising its marketing partners. Yet other major retailers handle such challenges with greater success. For example, it is comparatively rare to see spyware or adware promoting, defrauding, or attempting to defraud Amazon — even though Amazon spends nearly three times as much on marketing as VistaPrint ($344 million to $125 million).

What could VistaPrint do differently? For one, I question VistaPrint’s choice of marketing partners: As the preceding statistics indicate, I have repeatedly and widely seen spyware and adware sending traffic to many of the partners VistaPrint works with. VistaPrint might face less fraud if it favored marketing partners with a track record of successful supervision of their affiliates.

More generally, an affiliate currently faces little real downside to attempting to defraud VistaPrint. If an affiliate gets caught cheating, VistaPrint will terminate that affiliate, but I see little indication that VistaPrint exacts any meaningful penalty to make the affiliate (or the network providing that affiliate) regret its transgression. In Deterring Online Advertising Fraud Through Optimal Payment in Arrears, I suggest a different approach — paying affiliates more slowly so that they face greater losses if they are found to be cheating. Alternatively, VistaPrint might sue affiliates it learns are cheaters, as in eBay v. Digital Point Solutions and Lands’ End v. Remy.

Yet Keane’s remarks (“highly analytically driven fact-based decision-making”) reveal that VistaPrint is at least attempting to supervise its marketing partners to optimize its spending. How, then, could VistaPrint end up facing so much fraud? I suspect VistaPrint’s analytics actually lead the company astray. Consider the tactics presented above, from the perspective of the information easily available to VistaPrint’s marketing staff. Because these affiliates target users who are already interested in VistaPrint, the affiliates’ conversion rates are likely to be well above average. Moreover, because these affiliates incur limited costs, they can accept payments far below what Google might require. Thus, VistaPrint’s staff are likely to assess these affiliates favorably — without realizing that the traffic at issue is traffic VistaPrint would otherwise have gotten for free. Put differently: Although VistaPrint’s measurements may be very precise, they’re inaccurate because VistaPrint misunderstands the sources of affiliates’ traffic.

In attempting to prevent such fraud, VistaPrint should also examine its ad networks’ incentives. Ad networks often mark up affiliates’ fees: For every dollar VistaPrint is slated to pay to a given affiliate, that affiliate’s network takes another (say) $0.20. As a result, ad networks have a clear incentive to tolerate rogue affiliates: Networks make money from each sale credited to an affiliate, so ejecting rogue affiliates would directly reduce the network’s earnings.

The Big Picture

Spyware-based advertising fraud extends far beyond VistaPrint. Most merchants operating affiliate, CPA, or other conversion-contingent programs face similar fraud. But VistaPrint is a large and, purportedly, sophisticated advertiser. So VistaPrint could appropriately lead by example.

I’m overdue to present further examples of spyware and adware continuing to defraud major merchants. Historically my articles have tended to emphasize the largest US affiliate networks — Commission Junction, LinkShare, Performics. But there’s plenty of fraud through smaller networks too, as well as through networks based outside the US. I’ll present additional examples later this fall.

In January, an Anti-Spyware Coalition workshop asked “Is adware dead?” Some panelists responded substantially in the affirmative. But my AutoTester indicates otherwise. I’m pleased to see that big advertisers no longer advertise directly with major adware vendors. Yet a chain of indirection — adware sending traffic to one ad network, which forwards to another, then finally to an advertiser — continues to promote top brands. Furthermore, spyware-delivered banner farms and ad-loaders are becoming increasingly widespread. This month I saw adware still promoting American Express, Apple, and AT&T — to name just a few of the A’s. There’s plenty of work left to be done.

Typosquatting: Unintended Adventures in Browsing

Edelman, Benjamin. “Typosquatting: Unintended Adventures in Browsing.” Cybercrime Gets Personal, McAfee Security Journal (fall 2008): 34-37.

Typosquatting is the practice of registering domain names, identical to or confusingly similar to trademarks and famous names, in hopes that users will accidentally request these sites–whereupon they will receive, typically, advertisements. This piece presents the basic typosquatting business model, based on my analysis of more than 80,000 typosquatting domain names. I analyze the advertising intermediaries that make typosquatting profitable, and I assess the legislation and litigation that are beginning to put a check on this practice.

Debunking Zango’s "Content Economy" updated May 29, 2008

Zango often touts its so-called “content economy” — purportedly providing users access to media in exchange for accepting Zango’s popup ads. After four years of debunking Zango’s claims, I’ve come to suspect the worst — and my investigations of Zango’s media offerings confirm that Zango’s media library is nothing to celebrate. This article reports the results of my recent examinations. I show:

  • Widespread copyrighted video content presented without any indication of license from the corresponding rights-holders. Details.
  • Widespread sexually-explicit material, including prominent explicit material nowhere labeled as such. Details.
  • An audio library consisting solely of prank phone calls to celebrities (without the “music” Zango promises). Details.
  • Widespread material users can get elsewhere for free, without any popups or other detriments. Details.
  • Widespread material that content creators never asked to have included in any Zango library. Details.

Widespread copyrighted video content presented without any indication of license from the corresponding rights-holders

Many of the videos in of Zango’s video library are the work of major movie studios, TV networks, and other third parties that own and assert copyright in their respective works. These videos consistently appear without any statement of authorization (e.g. “used with permission”) or even the ordinary copyright notice. I therefore conclude that Zango’s site features these videos without authorization from the corresponding rights-holders.

Zango Offers Daily Show with Guest Chris Rock Zango Offers Daily Show w/ Chris Rock

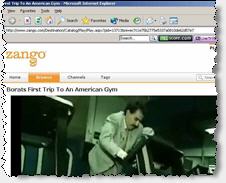
Zango Offers 'Borat' Zango Offers Borat

For many videos in Zango’s library, it is trivially easy to determine the video’s source. For example, text in the corner of Zango’s “Ashley Judd Nude Photoshoot” indicates the video comes from “Norma Jean & Marilyn” (1996, released on DVD by HBO Home Video). The title of Zango’s “Wild Things” suggests the video comes from the 2004 Sony Pictures movie by the same name; watching the video confirms the match. Zango’s “Girls Next Door Nude Compilation” begins with the distinctive Playboy logo. Zango’s “Chris Rock on the Daily Show” reproduces a video clip from Comedy Central’s Daily Show. It’s easy to find scores of other examples plainly labeled as well-known copyrighted works.

Other videos in Zango’s library are harder to identify — at least those without extensive entertainment industry experience. For example, I cannot easily determine the specific movie that included the scenes shown in Zango’s “Paris Hilton Striptease” or “Rachel Hunter in the Bathtub.” But the clips leave little doubt that they were filmed professionally and that the respective studios hold copyright in the resulting works. Similarly, I cannot easily determine the specific source of Zango’s “Branding Beat Down.” However, every frame of the video bears the distinctive Fox logo — indicating that the video originated with the Fox Broadcasting Company.

As to at least eight of the files in Zango’s library, I have specifically confirmed that Zango’s reproduction occurs without authorization from the underlying rights-holders. (Details below.) As to selected other files, I have sent inquiries to the corresponding rights-holders. I will update this page if I confirm whether Zango has properly licensed the content at issue.

Infringing videos are remarkably prominent in Zango’s video library. For example, as of May 27, Zango’s home page linked to “Borats First Trip To An American Gym” (s.i.c.). This clip was listed as the second most popular video in Zango’s entire content library, and it was placed in the top-center of Zango’s main www.zango.com web page, “above the fold” (within the portion of the page visible without using scroll bars). Yet the title of the video plainly indicates that the video contains the copyrighted work of others. Moreover, the video features the “DIVX Video” logo, indicating that DivX software was used to extract (“rip”) the video from a DVD. No authorized reproduction would be provided with a DivX overlay, so the presence of the DivX marker confirms that this video was reproduced without permission from the creators of Borat.

Other online video sites have been the target of major copyright litigation. For example, Viacom last year sued Google, alleging that “YouTube appropriates the value of creative content on a massive scale for YouTube’s benefit without payment or license.” In defense, Google points out that YouTube receives videos from independent — potentially granting Google immunity for these infringements due to the Digital Millennium Copyright Act‘s safe harbor for infringements occurring at the direction of users (17 USC 512(c)(1)).

Unlike YouTube, Zango’s video library offers no prominent “upload” function. Some of Zango’s videos arrive through the Revver video-sharing service (discussed below), probably originating with a variety of independent users. But many of the copyrighted videos Zango offers reside on Zango’s servers, not on Revver servers. (For example, all eight of the sexually-explicit videos linked in the first paragraph of the next section are hosted on Zango servers.) Because Zango offers no “upload” function by which ordinary users could have put videos onto Zango’s site, it therefore appears that these videos were provided by Zango or its agents, not by independent users. If so, Zango will not find protection in the DMCA’s safe harbor for infringements caused by users.

Moreover, even if Zango’s videos were provided by independent users, the circumstances of the reproduction seem to render Zango ineligible for the DMCA safe harbor. For one, the safe harbor requires that Zango lack actual knowledge of the infringements. But the infringing videos were obvious and self-evident, not just from their titles and contents, but also from their prevalence in featured results Zango chose to highlight. In addition, the safe harbor requires that Zango not receive a financial benefit directly attributable to the infringements. But Zango used these videos to induce users to download its popup-generating software, a financial benefit that is directly attributable to the infringing videos. (Consider the case of a user who installs Zango in response to solicitation offering a specific copyrighted video clip. Example.) Furthermore, Zango has the right and ability to control the infringement (e.g. by removing the infringing videos). Because Zango’s financial benefit can be directly tracked to a specific infringement, and because Zango has the right and ability to prevent such infringement, Zango seems to fail the test in 17 USC 512(c)(1)(B).

Zango may claim that its videos are fair use. The Copyright Act sets out a four-factor test for determining whether reproduction of a copyrighted work is permissible, despite lack of authorization from the rights-holder. The fair use test calls for considering 1) the purpose and character of the use (e.g. whether commercial or nonprofit), 2) the nature of the copyrighted work, 3) the amount and substantiality of the portion used, and 4) the effect of the use upon the potential market for the work. Factor one is easy: Zango’s use is clearly commercial, which tends to cut against a finding of fair use. Zango might claim that its presentation of excerpts (rather than entire movies) supports a finding of fair use under the third test — but Zango exactly chooses what it views as highlights (e.g. the explicit portions of full-length movies), yielding clips with a greater than usual effect on the potential market for the underlying works. In short, a fair use defense is at best uncertain.

Wide-scale copyright infringement could expose Zango to substantial liability. The Copyright Act provides for statutory damages of “not less than $750” per violation. My examination indicates Zango is reproducing (at least) hundreds of copyrighted videos without any statement of authorization. Furthermore, such videos have surely been downloaded repeatedly — giving rise to potential statutory damages that could easily reach seven digits or more.

Widespread sexually-explicit material, including prominent explicit material nowhere labeled as such

Celebrity Videos Featured by Zango Celebrity Videos Featured by Zango

Prominent Video - Explicit but Unlabeled
Prominent Video – Explicit but Unlabeled

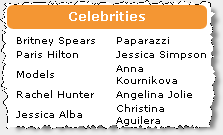
Browse Zango’s video library, and it’s easy to find sexually-explicit video. As shown in the first inset image at right, the bottom-right corner of each Zango “Browse” page gives a list of celebrities — each of them female, each featured in various states of undress. Among other explicit videos of these celebrities, Zango offers “Britney Spears See Thru“, “Britney Spears Black Dress Upskirt“, “Paris Hilton Striptease“, “Rachel Hunter in the Bathtub“, “Jessica Alba’s Chest and You“, “Jessica Simpson Nipple Slip“, “Anna Kournikova Panties Oops“, and “Angelina Jolie Sex Scene.”

The titles and descriptions of many of Zango’s videos suggest that their subjects were unwilling participants. See e.g. “nipple slip” and “upskirt” above, as well as additional videos like Zango’s “Arab wife’s sexy dance secretly taped” and Zango’s “Girlfriend Finds Hidden Camera.”

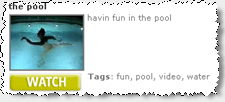
Through its placement and labeling of sexually-explicit videos, Zango creates a substantial risk that users will receive explicit materials they did not seek. For example, on May 24, I clicked “Browse” to flip through Zango’s content library. Using Zango’s default sort, the third video was entitled “the pool” with comment “havin fun in the pool” (s.i.c.). (Screenshot of the link from within Zango’s video library.) This title and comment give no indication that the resulting material is explicit. But clicking the “Watch” button immediately yields a large video showing two male adults swimming nude, then exiting the pool (entirely disrobed). As best I can tell, Zango did nothing to alert users to this explicit material, nor does Zango prevent (or even discourage) children from viewing such material.

Zango’s May 24 “the pool” video was not a mere anomaly. The same video remained linked in the same way in my tests on May 25 and 26, and on portions of May 27.

In litigation documents, Zango last week claimed that it never distributes explicit material to those do not want it. In particular, Zango argues: “Zango never sends unwanted links to pornography web sites” and “Zango only directs adult-oriented advertisements to a user after that user, by his own behavior, has demonstrated interest in such content.” I disagree. The preceding paragraphs offer a counterexample — Zango prominently providing a link to sexually-explicit materials, and provideing that links to users who never demonstrated interest in any such content. Zango may claim that these links tout videos — not a “web site” as in the first quoted sentence. Alternatively, Zango may claim that the links are not “advertisements” — hence beyond a strict reading of the second quoted sentence. But the underlying contradiction remains: Zango says it doesn’t provide pornography except when users seek it; yet in fact Zango does sometimes deliver explicit materials unrequested.

That Zango funds and distributes sexually-explicit materials is well-known. See e.g. the Sunbelt Blog’s February 2008 conclusion that “80% of [Zango’s] business comes from Seekmo, the porn side of its business.” See also Sunbelt’s off-hand November 2006 remark that “hardcore porno videos [are] funded through Zango Seekmo installs.”

But the scope of explicit materials within Zango’s video library is quite striking. Consider the first page of Zango’s library listings for Angeline Jolie. Beyond the “sex scene” video linked above, the listings also include “Angelina Jolie Taking a Bath”, “Angelina Jolie Under the Sheets”, “Angelina Jolie in Bra & Panties”, “A fairly long nude scene staring Angelina Jolie” (s.i.c.), “Angeline Jolie Getting It On”, “Angelina Jolie Nip Slip”, “Angelina Jolie Hardcore”, and “Angelina Jolie Dominatrix”, and “Angelina Jolie Hot On The Runway.” That’s ten explicit results out of twenty links — suggesting that explicit materials are remarkably widespread on Zango’s site.

The initial version of this article also flagged Zango’s “Nice But” (s.i.c.), a video that on May 27 occupied the fourth-most prominent position in Zango’s “Browse” listings. The thumbnail image of this video appeared to feature a full-screen display of a man’s naked buttocks, filling the entire screen. In a follow-up, Zango points out that in fact, the video shows an extreme close-up zoom of of two hands. So this image and video are not actually explicit. Yet a viewer merely flipping through Zango’s listings would nonetheless see an image that is, by all indications, explicit. The title “but” (s.i.c.) and the keyword “naked,” both adjacent to the thumbnail, reinforce the user’s perception of having seen an unrequested explicit image. Although the image is not actually explicit, the image’s content, placement, and labeling make it likely to leave users with the same feeling as an unrequested image that is actually sexually explicit: In both instances, a viewer who merely sees the image and does not watch the video will think he has seen an unwanted explicit image. In my view, Zango errs in mocking this harm. To the users who Zango tricks, the harm is perfectly real.

Zango’s audio library consists solely of prank phone calls to celebrities

Zango Offers Prank Phone Call Recordings Zango Offers Prank Phone Call Recordings

Zango’s content library offers three types of media: Videos, screensavers, and audio. Despite Zango’s much-touted “content economy,” Zango offers just eight audio clips. And although Zango’s “About Zango” description promises to provide free access to “music,” in fact all eight of these audio files are recordings from talk radio — just voices, with no music at all.

All eight of Zango’s audio recordings share a common theme: Prank phone calls to celebrities. In each, a caller pretends to be someone famous (e.g. the Prime Minister of Canada), and calls a celebrity (e.g. Bill Gates) under the guise of a bona fide discussion. The caller proceeds to berate the celebrity (e.g. by criticizing the features and reliability of Windows).

A comment in several of the videos reveals the source of the recordings: The Masked Avengers, which Wikipedia describes as “a Canadian radio duo … of disk jockeys and comedians Sebastien Trudel and Marc-Antoine Audette, known for making prank calls to famous persons by pretending to be government officials or officers in charitable organizations.” I wrote to Mr. Trudel, who confirmed to me that he has not granted Zango any license to use or reproduce these clips.

After placing these recordings in its content library, Zango further syndicates the materials onto Zango’s partner sites. For example, celebsprankd.com (screenshot) features all eight recordings, but requires users to install Zango before listening. Whois reports that Celebsprankd comes from the Vancouver, B.C. advertising firm Neverblue Media — a conclusion confirmed by the presence of the Neverblue.com web server at the same IP address. Neverblue describes itself as a “leading … online marketing company” offering “premier” advertising and “solid business leads” — claims arguably inconsistent with distributing and profiting from prank phone calls, not to mention distributing Zango. (But these recordings aren’t Neverblue’s only tie to Zango. This month alone, my Automatic Spyware Tester found eleven incidents of Neverblue affiliates buying popup traffic from Zango. I’ve also found dozens more incidents as to Neverblue affiliates buying traffic from other spyware.)

What of Zango’s distribution of these prank call recordings? With so few clips yet such prominent placement (including five of these eight audio recordings featured on Zango’s home page), senior Zango staff surely know what the files contain. Does Zango support prank phone calls? Wasting celebrities’ time under false pretenses? Recording phone calls without permission, even in states that specifically require such permission? It’s hard to reconcile these practices with Zango’s supposed reforms.

Widespread material users can get elsewhere for free, without any popups or other detriments

Much of Zango’s content is available elsewhere without charge and without installing any software that tracks online behavior or shows popup ads. For example, clicking Zango’s “Browse” tab and retaining defaults, every single video on the first page of results is syndicated from Revver. Users could just as easily get these videos directly from Revver, as receive them from Zango. But if users watched these videos at Revver, Zango’s software would not track their web browsing and searching, and users would not receive Zango’s popup ads.

Zango Falsely Claims that Uninstallation Eliminates Content Access Zango Falsely Tells Its Users:
“Uninstallation … eliminates content access”

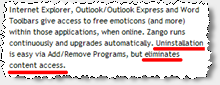
Furthermore, Zango makes untrue claims about the necessity of its software. For example, Zango claims that “uninstallation … eliminates content access.” It does not. For files hosted at Revver, installation of Zango is not necessary to watch the videos in the first place, and uninstallation does not interfere with watching the videos later. Moreover, even many Zango-hosted files can be accessed without installing Zango, or after uninstalling Zango. For example, Zango’s “Chris Rock on the Daily Show” is actually just a standard Windows Media Video (WMV) distributed from the following URL: preview.licenseacquisition.org/123/1054944882.36393/yikers_chris_rock_on_the_daily_show.wmv . Zango’s “Borats First Trip To An American Gym” (s.i.c.) is preview.licenseacquisition.org/123/1054944854.02531/yikers_borats_first_trip_to_an_american_gym.wmv . Similarly, Zango’s “Bill Gates Gets Pranked” is a WMA hosted at preview.licenseacquisition.org/13/12295/12295.wma . Any user who knows these URLs can easily receive the corresponding files — without ever installing Zango, or after uninstalling Zango. Zango ought not claim otherwise.

Presenting material that content creators never asked to have included in any Zango library

By syndicating videos from Revver, Zango causes its video library to feature materials that content creators never asked to have associated with Zango in any way.

Zango’s syndication of Revver videos has prompted numerous complaints content creators who post videos to Revver. For example, Chris Pirillo asked why his videos are appearing on Zango. (“I don’t remember giving Zango permission to push crapware on my behalf.”) Revver forum user JPPI pointed out the irony of Zango claiming his videos were “FREE, thanks to Zango” when in fact the videos were free all along (even before Zango syndicated them). Revver forum user David complained that it is “kinda deceptive” (s.i.c.) “to make it sound like Zango was the one who made the video free.”

In response, Revver Vice President Asi Behar agreed to ask Zango to remove any Revver videos that Revver authors specifically so designate. But such removals do nothing to cure the deception of Zango requiring that users install its software before watching materials widely available elsewhere for free. Furthermore, such removals do nothing to protect Revver content creators who are unaware of Revver’s relationship with Zango. The word “Zango” appears nowhere on Revver’s official web site (as distinguished from Revver’s forums and some Revver-hosted videos). Thus, a Revver content creator has no easy way to learn about Revver’s relationship with Zango — not to mention learn of the option to request exclusion from Zango.

Zango’s syndication of Revver videos risks tainting the good name of Revver content creators. Consider a user who searches for a Revver video and finds that video hosted at Zango (just as Chris Pirillo did last year). The user may mistakenly conclude that installing Zango is in fact necessary to watch the video. If so, the user is likely to end up with a negative view of the underlying content creator — mistakenly concluding that, e.g., Chris Pirillo has partnered with Zango or endorses Zango’s activities. Revver forum complaints indicate that numerous Revver users share this concern. Yet Revver continues to syndicate videos to Zango without first checking with content creators.

Zango’s problems in context

Last week, Zango was one of four finalists for the Software & Information Industry Association’s CODiE Best Video Content Aggregation Service. In my view, that award is misguided: Far from deserving praise, Zango should be criticized and shunned for reproducing others’ copyrighted work without any apparent license to do so, showing sexually-explicit material unrequested, and offering users a lousy value by bundling extra ads with content users could get elsewhere for free.

Meanwhile, Zango continues litigation with Kaspersky. Recall: Kaspersky blocked Zango’s software from installing; Zango sued; Kaspersky successfully defended on the grounds that the Communications Decency Act, 47 USC 230, immunizes Kaspersky’s behavior because Kaspersky is an “interactive computer service provider” blocking material that, in its subjective opinion, is “objectionable.” In Zango’s appeal, Zango claims its software is not “otherwise objectionable” (brief pages 12-15; PDF pages 17-20). If it’s not objectionable to show explicit material unrequested — not to mention to infringe copyrights on a massive scale, and to insert extra ads around material available elsewhere without such ads – then I don’t know what is.

Finally, I’m often asked whether Zango continues the behaviors I previously reported. Installing through sneaky fake-user-interface pop-up ads that mimic the appearance of official Windows dialog boxes (as I reported last summer)? Yes. I made a fresh video showing such installations just last week.Defrauding advertisers through popups that cover merchants’ sites with their own affiliate offers(as I reported last spring, in September 2005, in summer 2004, and otherwise)? Definitely. This month alone, I reported six Zango incidents to just one of my advertiser clients — not to mention scores of other incidents targeting other web sites and advertisers. Zango repeatedly claims its problems are all in the past, but my hands-on testing continues to indicate otherwise.

Coupons.com and TRUSTe: Lots of Talk, Too Little Action updated March 20, 2008

Six and a half months ago, I reported a variety of bad practices at Coupons.com. Key among my concerns: Coupons.com stored data in deceptive filenames and registry entries designed to look like part of Windows — with names like c:\WINDOWS\WindowsShellOld.Manifest.1 and HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Controls Folder\Presentation Style. Furthermore, Coupons.com failed to remove these files upon a user’s specific request to uninstall.

Because Coupons.com was certified by TRUSTe Trusted Download, I reported these behaviors through TRUSTe’s Watchdog form. TRUSTe investigated and, it claimed, required Coupons.com to make changes. Last month, TRUSTe declared success: “Coupons, Inc. rolled out a number of significant changes …. To improve registry key and naming (s.i.c.), the new version of the software uses an improved security scheme that writes only one registry key placed in a typical location, named in an appropriate manner.” TRUSTe concluded by giving itself a pat on the back — calling this sequence “an excellent outcome” in that “[a] user found a problem, filed a complaint, and TRUSTe worked with the Participant to make necessary corrections.”

I wanted to see for myself whether TRUSTe’s oversight is as effective as TRUSTe claims. So I downloaded Coupons.com’s current software onto an ordinary computer in my lab. (I couldn’t use a VMware virtual machine because Coupons.com detects VMware and refuses to install.) To my dismay, Coupons.com’s software continued to create the same deceptively-named files and registry keys I reported in August:

c:\WINDOWS\uccspecc.sys
c:\WINDOWS\WindowsShellOld.Manifest.1
HKEY_CLASSES_ROOTManifest.Template.1shellex
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\uccspecc
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Controls Folder\Presentation Style
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\EnableAutoTrayHistory
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\UrlDecoding

I prepared a screen-capture video to confirm and memorialize the deceptively-named files and registry keys. (My video begins by showing the New York Times front page, to demonstrate the date of testing.)

I then used Control Panel – Add/Remove Programs to attempt to uninstall Coupons.com’s software. I found that the specified files and registry keys all remained in place — even though TRUSTe further promised that “[t]he new version uninstaller removes the files.”

What’s going on? Maybe TRUSTe tested a different version of Coupons.com’s software than the version offered to the public. Maybe Coupons.com posted the wrong file. But whatever the reason, TRUSTe’s claims are inconsistent with my test results.

TRUSTe’s Oversight and What to Do Next

My testing indicates that Coupons.com has not made the changes TRUSTe specified. In particular, Coupons.com continues to use multiple registry keys and filenames with intentionally deceptive locations and names — exactly contrary to TRUSTe’s claim that “only one registry key” is used and that it is placed in a “typical location” with an “appropriate” name. Furthermore, Coupons.com leaves these files and registry keys after uninstall — exactly contrary to TRUSTe’s claim that the new uninstaller “removes the files left behind.”

Far from TRUSTe’s self-congratulatory rhetoric, Coupons.com’s practices reflect badly on TRUSTe: Despite clear violations widely reported 6+ months ago and a supposed investigation by TRUSTe, the problems continue to this day.

Worse, through two different channels, TRUSTe has falsely told users they can trust Coupons.com. First, Coupons.com has continuously remained on TRUSTe’s Trusted Download “whitelist” despite my initial report. That is, TRUSTe continued to certify Coupons.com even when TRUSTe knew of Coupons.com’s deceptive practices and even when there was no dispute that the practices were ongoing. A better strategy, per my September 2007 recommendation, would be to suspend violators until they have fully corrected their practices. Otherwise, a user looking at the “whitelist” cannot know which companies are truly in good standing, versus which have fallen short and are must make improvements.

Second, TRUSTe has posted announcements (1, 2) that falsely characterize the status of Coupons.com’s improvements: In September TRUSTe promised the changes would be “completed within 90 days” — but in fact, they’re still not in place 180 days later. In February TRUSTe proclaimed the changes complete — but in fact Coupons.com’s software still has the same problems I previously identified.

These failings go to the core of TRUSTe’s promise to “make privacy your choice.” TRUSTe claims to be giving users the information they need to make informed decisions. However, TRUSTe’s information is systematically in error — to the benefit of the companies that pay TRUSTe to get certified, but to the detriment of any users who mistakenly rely on TRUSTe’s investigations.

An Additional Violation: Executable Software Left Behind After Uninstall

My recent tests also revealed a new file I hadn’t noticed in prior tests: c:\WINDOWS\system32\cpnprt2.cid. How did I miss this file? It appears only after a user first prints a coupon — not when a user initially installs Coupons.com software. So this file wasn’t created in my prior testing.

Despite the file’s unusual .CID extension, the file is actually a DLL containing executable code. Although “cpnprt” bears some relationship to Coupons.com’s product name (“CouPoN PRinTer”), I can see no proper reason to place this file within c:\WINDOWS\ rather than in c:Program Files\Coupons with Coupons.com’s other files. So Coupons.com’s improper file locations include not only data files (like those listed above), but also executable code.

Moreover, I see no proper reason for calling the file a .CID rather than the DLL that it is. This misnaming serves to further obfuscate the file’s purpose and to prevent typical users from determining that the file contains executable software code.

In separate testing, I confirmed that this file remains on a user’s computer even after the user removes Coupons.com’s software. (This too is shown in my screen-capture video.) So Coupons.com leaves behind not just data, but also executable software. Leaving executable code stands starkly in contrast to Coupons.com’s license agreement which mentions only that “license keys wil not be removed when the Software is uninstalled” — but says nothing about software code left behind.

Coupons.com violates TRUSTe Trusted Download requirements when it leaves executable code after a user’s uninstall request. Trusted Download rule 7.(a)(ii) requires a complete uninstall and allows only limited exceptions — none of them applicable here. (The closest exception allows “properly disclosed anti-fraud … measures” — but this practice is not “properly disclosed,” nor is surviving executable code required to track whatever practices might conceivably be at issue.) Coupons.com’s cpnprt2.cid file therefore constitues another violation of applicable Trusted Download rules.

Coupons.com’s Ongoing DMCA Litigation with John Stottlemire

Last summer I mentioned Coupons.com’s misguided DMCA litigation against John Stottlemire. The case drags on: John’s blog reports ongoing events, including John’s motion to dismiss, the court’s granting of that motion, Coupons.com’s second amended complaint, and John’s second motion to dismiss.

My view remains that this litigation is ill-advised for Coupons.com: Coupons.com has too much work to do, improving its own software and its own business practices, to waste management time and attention on pursuing a user who merely helped others remove deceptively-named files and registry keys. Coupons.com has nothing to gain here: Even if Coupons.com can force John to stop telling users how to remove unwanted Coupons.com software, others will immediately pick up where John left off.

There’s plenty more to be said about the case — especially, concern at using the DMCA to stifle useful public-interest discussion of how to remove unwanted software from an ailing computer. But I’ll leave that to others: TechDirt, Wired, and various bloggers.

Update (March 20, 2008)

TRUSTe’s Response and My Hands-On Testing

In a March 19 posting, TRUSTe claims that the issues described above reflected Coupons.com software available only between March 15 and March 17. But TRUSTe stands behind its February report that Coupons.com had “addressed [the] concerns” TRUSTe previously raised based on my prior article. I emphatically disagree. In particular, my hands-on testing, memorialized in video records, clearly demonstrates that Coupons.com continues to violate TRUSTe’s prior instructions and applicable TRUSTe rules. Consider my March 19 video:

1. At 0:02, I demonstrate the current date and time. I then run an InCtrl scan to record existing files and registry keys.

2. At 1:15, I begin to browse the Coupons.com site, and at 1:25 I attempt to print a coupon. 

3. At 1:33, I begin to install the Coupon Printer program, including providing a name and email address when requested (2:20). 

4. At 2:55, I browse c:\WINDOWS\ to show the newly-created and deceptively-named CID file (as discussed above).  I then proceed to find a file by the same name placed in c:\WINDOWS\system32 also.

5. At 3:30, I rerun Inctrl to identify newly created files and registry keys.  The results are visible beginning at 5:35.  I notice the HKEY_CLASSES_ROOT\English.cpl registry key in the listing (5:45), and at 5:50 I use Regedit to confirm that the key is indeed present. 

6. At 6:30, I request an uninstall in the usual way (Control Panel – Add or Remove Programs).  I then show that deceptively named file remains in c:\WINDOWS\ (7:14) and c:\WINDOWS\system32 (7:08); despite my uninstall request, these files were not removed.  I show that the deceptively-named registry key remains also (7:02). 

The Violations Revealed by My Hands-On Testing

The preceding video presents three separate different violations of TRUSTe rules and of TRUSTe’s prior representations of Coupons.com’s supposed compliance:

A) Step 4 shows a deceptively-named file placed on a user’s computer. There is no proper reason to call this file a .CID rather than the DLL that it is. Nor is there any proper reason for Coupons.com to place the same file in both c:\WINDOWS\ and c:\WINDOWS\system32. Indeed, my tests indicate that Coupons.com sometimes uses one of those folders, sometimes the other, and sometimes both — a randomization procedure with no proper purpose, but with the natural effect of confusing users and hindering detection and removal.

These deceptive filenames are exactly contrary to TRUSTe’s claim that it has resolved the problem of Coupons.com’s “inappropriately-named files.” These deceptive filenames and randomized locations also violate TRUSTe rule 14(e)(v), which prohibits “using randomized or intentionally deceptive file names … for the purpose of avoiding detection and removal.”

B) Step 5 shows a deceptively-named registry key. Coupons is not, and is not commonly known as, “English.cpl.” Indeed, the file extension “CPL” indicates a Control Panel applet or extension — but Coupons.com offers no such extension. Neither does Coupons.com have any proper basis to place its configuration data in HKCR — a registry area reserved for file extensions and COM class registrations. Rather, Coupons.com clearly chooses this area to store its configuration data because users would never think to look here. Indeed, in repeated testing, I found that Coupons.com sometimes used other keys instead. For example, in a separate video early on March 19, I found that Coupons.com used HKCRWeb.Template.URL rather than HKCREnglish.cpl. Randomization of registry keys further confirms that Coupons.com uses these registry locations to avoid detection.

These randomized and intentionally-deceptive registry keys are exactly contrary to TRUSTe’s claim that all registry keys are “placed in a typical location [and] named in an appropriate manner.” These deceptive filenames and randomized locations also violate TRUSTe rule 14(e)(v), which prohibits “using randomized or intentionally deceptive … registry entries for the purpose of avoiding detection and removal.”

C) Step 6 shows that Coupons.com fails to remove all its files and registry keys upon a user’s specific request to uninstall.

The retention of these files is exactly contrary to TRUSTe’s claim that the “new version uninstaller removes the files left behind.” The retention of these files also violates TRUSTe rule 7.(a)(ii), requiring a complete uninstall and allows only limited exceptions — none of them applicable here.

The retention of these files also violates Coupons.com’s license agreement — which mentions only that “license keys will not be removed when the Software is uninstalled,” but says nothing about software code left behind. Although TRUSTe’s Trusted Download rules do not specifically require that a company comply with the provisions of its license agreement, I take such compliance to be so obvious that it does not require a specific mention. Coupons.com’s violation of representations in its own license agreement therefore constitutes yet another violation of TRUSTe requirements.

Additional Violations: Coupons.com Retrieving Windows CD key and system serial numbers

In testing using API and registry-monitoring tools, I have determined that Coupons.com retrieves a wide variety of sensitive Windows registry keys and computer configuration settings including Windows Product ID, Windows CD key, motherboard serial number, and hard drive serial number. These numbers serve to identify a specific individual computer, and these numbers persist over the lifetime of a computer. Coupons.com. These practices stand in sharp contrast to Coupons.com’s representations to users:

  • The Coupons.com “promo” promises that “The Coupon Printer does not gather or ask for any personal information about … your computer.” Yet my testing indicates that Coupons.com gathers detailed computer-specific information about each computer on which it is installed.
  • Coupons.com’s privacy policy similarly promises that “The Coupons, Inc. software … only collect[s] information about what coupons have been printed and redeemed from your computer” — again, directly at odds with my observation that Coupons.com collects far more information.
  • Coupons.com’s license agreement discloses this information collection only by admitting that the “software uses anonymous, assigned numbers and/or anonymous information about your computer or device.” But the numbers at issue are not anonymous: These numbers identify a specific individual user based on the user’s unique and unvarying Windows CD key, motherboard serial number, and hard drive serial number. TRUSTe rule 1.qq defines such information to be pseudonymous (“information that may correspond to a person [such as] machine ID”), while rule 1.i defines anonymous information to exclude all pseudonymous information. Coupons.com thus errs in characterizing these numbers as “anonymous.” Moreover, Coupons.com errs in disclosing this data collection practice only in its license agreement; because this practice speaks to user privacy, it belongs in Coupons.com’s privacy policy.

TRUSTe’s Ineffective Investigation and Response

TRUSTe staff could have identified each of these defects when they tested Coupons.com software in February. Instead, TRUSTe staff issued a boilerplate endorsement — failing to identify shortcomings that would have been apparent in any careful analysis.

Remarkably, even after my post above and even after John Stottlemire’s March 18 post detailing many of these issues in great detail, TRUSTe nonetheless described Coupons.com’s problems as “corrected.” TRUSTe even called this process “a good example of how the [Trusted Download] program should work.” I emphatically disagree: Coupons.com remains flagrantly in violation of TRUSTe’s instructions and rules, and TRUSTe has failed either to obtain suitable corrections or to eject Coupons.com from its whitelist.

To this day, Coupons.com is in breach of TRUSTe’s rules, and TRUSTe knows it. Yet Coupons.com remains listed on TRUSTe’s whitelist as if its practices are beyond reproach and as if the company is in good standing vis-a-vis TRUSTe’s rules. That’s outrageous, and users should demand better.

Delaying Payment to Deter Online Advertising Fraud

In a new article, I introduce an alternative method of fraud prevention for certain online advertising systems. By delaying payments, a merchant or network differentially harms bad affiliates (who rightly worry they may get caught) without unduly harming good affiliates (who know they’ll get paid, and who receive a bonus in compensation for the delay). With a suitable delay, a merchant or network can deter many bad affiliates while retaining the good.

My working draft:

Optimal Deterrence when Judgment-Proof Agents are Paid in Arrears – with an Application to Online Advertising Fraud

Details on my approach, including initial data on merchants’ and networks’ current payment terms.

(update: published as Edelman, Benjamin. “Deterring Online Advertising Fraud Through Optimal Payment in Arrears.” Financial Cryptography and Data Security: Proceedings of the International Conference (September 2009). (Springer-Verlag Lecture Notes in Computer Science.))

Critiquing C-NetMedia’s Anti-Spyware Offerings and Advertising Practices

Not every “anti-spyware” program is what it claims to be. Some truly have users’ interests at heart — identifying and removing bona fide risks to privacy, security, stability, or performance. Others resort to a variety of tricks to confuse users about what they’re getting and why they purportedly need it.

This article reports the results of my examination of anti-spyware software from C-NetMedia. I show:

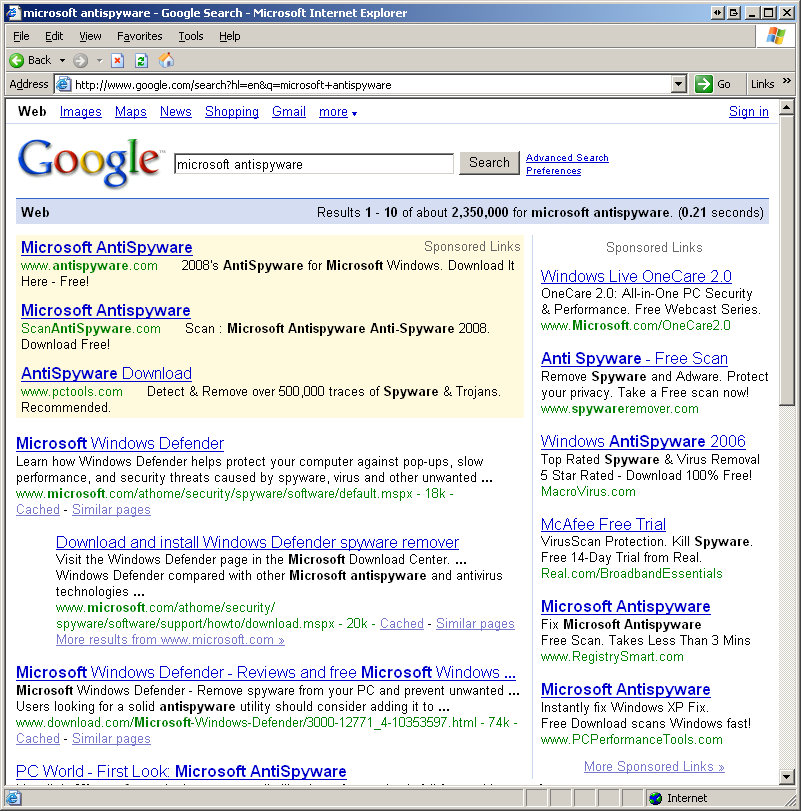
  • Deceptive advertising, deceptive product names, and deceptive web site designs falsely suggest affiliation with security industry leaders. Details.
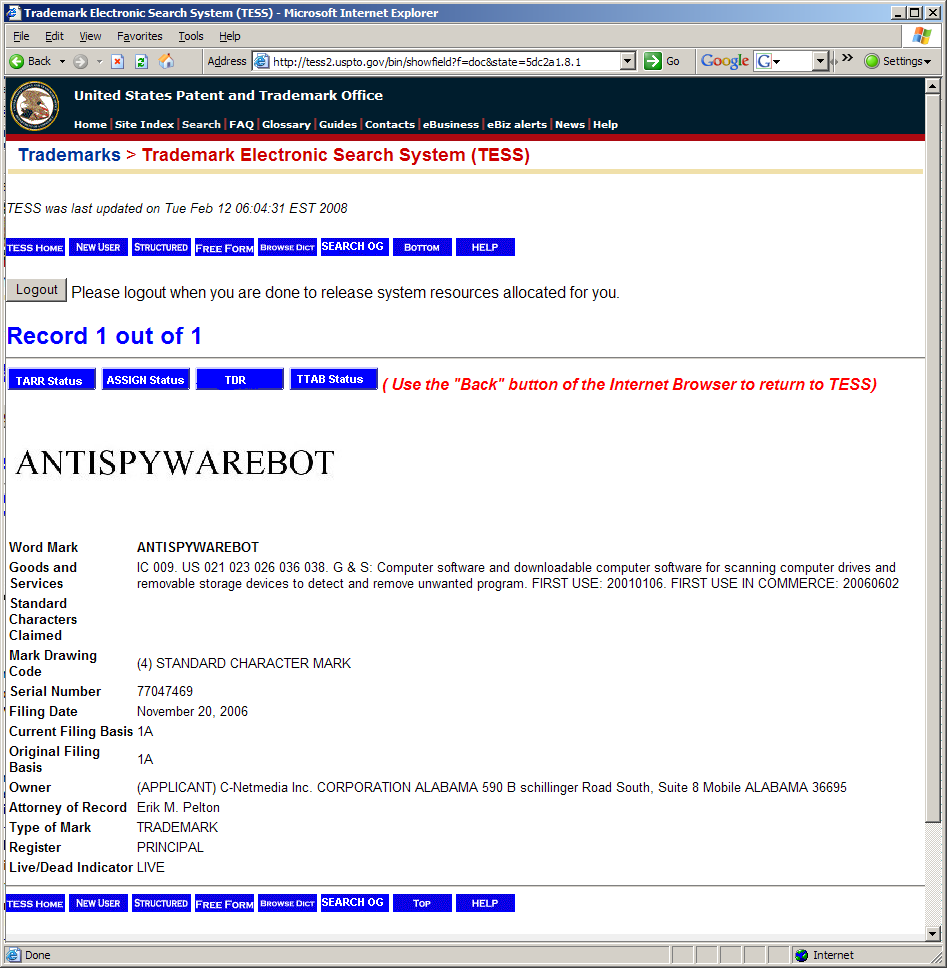
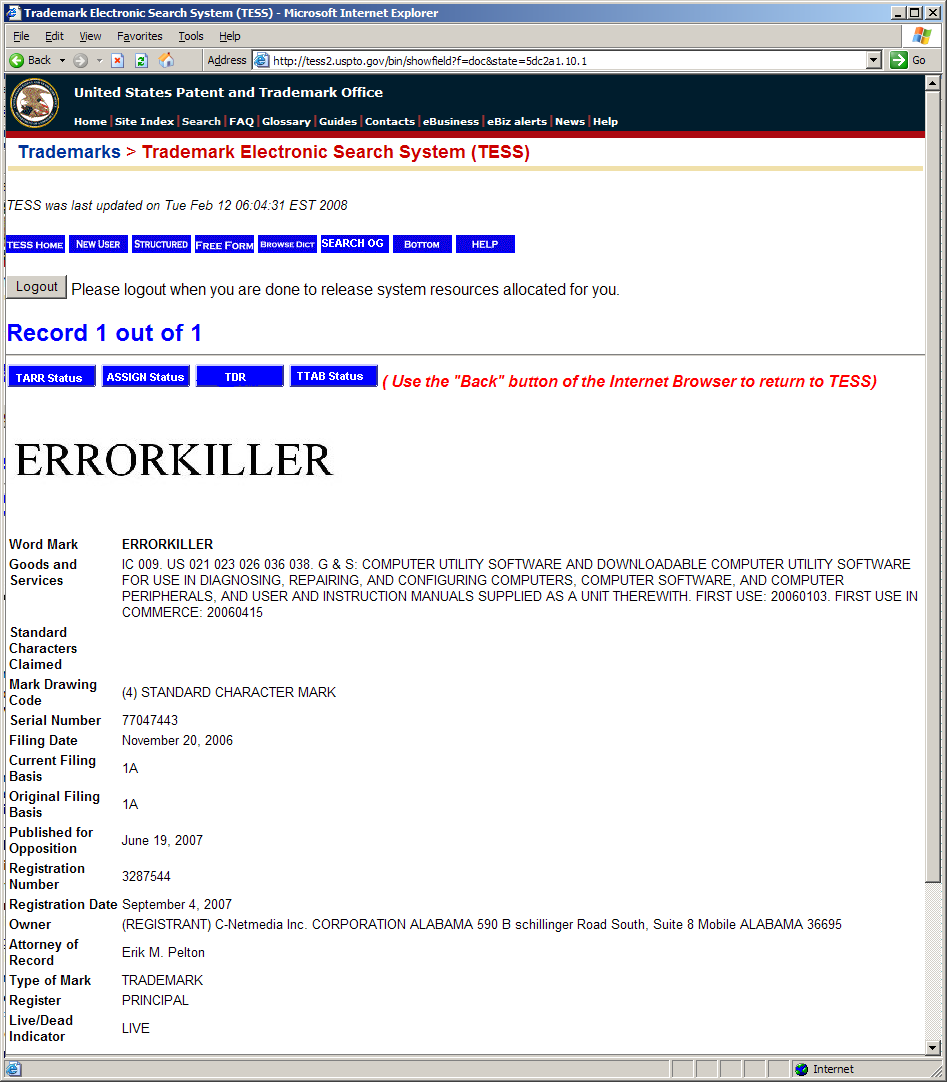
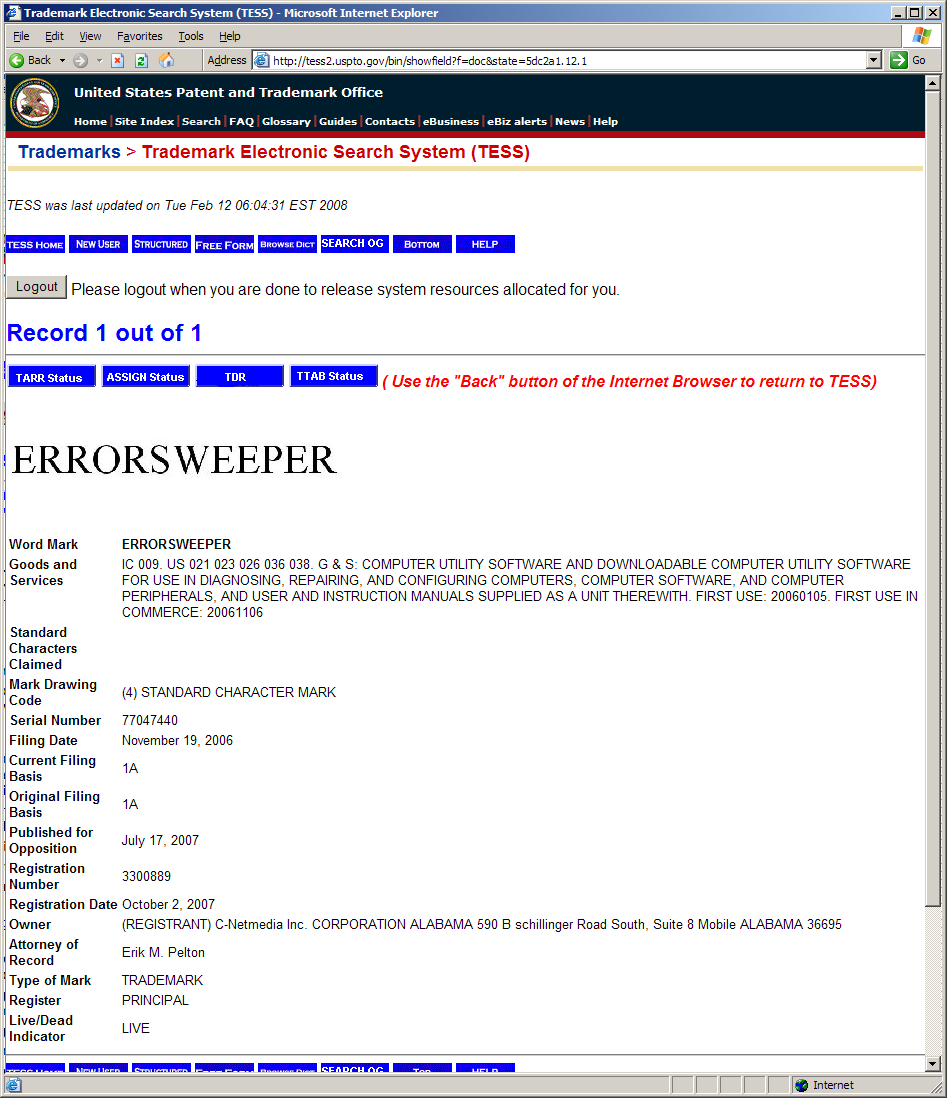
  • The use of many disjoint product names prevents consumers from easily learning more about C-Net, its reputation, and its practices. Details.
  • High-pressure sales tactics, including false positives, overstate the urgency of paying for an upgraded version. Details.

Note that C-NetMedia is unrelated to the well-known technology news site CNET Networks. Details.

Deceptive advertising, deceptive product names, and deceptive web site design falsely suggest affiliation with security industry leaders.

Some C-NetMedia products are marketed using practices, keywords, labels, and layouts that falsely suggest they come from security industry leaders. This suggestion comes from both the actions of C-Net itself, as well as from the actions of C-Net’s marketing partners.

Google Shows Deceptive Ads for C-Net's Products
Google Shows Deceptive Ads for C-NetMedia’s Products

Consider the top three ads for a Google search for “Spybot”, a popular early anti-spyware program (full name “Spybot Search & Destroy”). As shown at right, the top three ads each specifically mention “Spybot” — the first two, in directory names; the third, in its domain name. Furthermore, all three ads also include the distinctive and original phrase “Search & Destroy” that specifically describes the genuine Spybot product. Yet in fact each of these three ads takes users to the unrelated site spywarebot.com (emphasis added) (screenshots: 1, 2, 3). Clicking the first ad immediately takes a user to spywarebot.com via the ClickBank advertising network. As to the second and third ads, traffic flows through independent “landing page” sites which in turn show ClickBank links to promote Spywarebot. These landing pages are hosted on the deceptively-named domains named spybot-sd-info.com and www-spybotcom.com — each further (but falsely) suggesting an affiliation with the genuine “spybot” product.

C-NetMedia partners similarly fill top ad spots for a search for “Ad-Aware”, another well-known anti-spyware program. The top ad promotes C-Net’s adwarealert.com — a name particularly likely to confuse users because the ad’s title and domain differ from the user’s request by just a single letter. The first ad takes the user to adwarealert immediately, while the second ad takes users to a www-ad-ware.com landing page which also promotes adwarealert.com (again via ClickBank).

Other deceptive C-NetMedia partners pervade search results for spyware-removal search terms. See e.g. “Spybot-free.com” using distinctive “Spybot” “Search & Destroy” marks to promote C-Net’s spywarebot.com. See also C-Net’s Registrysmart.com advertising with ad title “Microsoft Antispyware” in Google results for searches on “Microsoft Spyware”. Because the Registrysmart ad title touts “Microsoft Antispyware”, users might reasonably think the ad will yield an official Microsoft site that actually provides the free “Microsoft Antispyware” product. But in fact the link leads only to a C-Net site with paid products.

C-NetMedia may claim that these ads were placed by affiliates. But the actions of these affiliates are prominent — occurring on search terms as well-known as “Spybot” and “Ad-Aware.” These actions are also longstanding: My October 2006 False and Deceptive Pay-Per-Click Ads shows that some of these ads have continued for more than a year. Furthermore, these affiliates act for C-Net’s benefit, and C-Net has the right and ability to monitor them, to oversee their activities, and to limit their efforts as it sees fit. Finally, FTC litigation confirms that companies can be liable for the actions of their affiliates and marketing partners. See e.g. US v. APC Entertainment (advertiser liable for sexually-explicit unsolicited commercial email sent by its affiliates), In the Matter of Zango, Inc. (advertising software company liable for nonconsensual and deceptive installations of its software by its partners), In the Matter of Direct Revenue LLC (same).

C-NetMedia’s involvement in these advertising practices is heightened by C-Net’s own selection of product names. C-Net, not its affiliates, chose product names so close to established market leaders — names that invite consumer confusion. C-Net furthers the confusion by calling its products “official” (e.g. “The Official Ad-Ware Client“, emphasis added) when there is no meaningful sense in which C-Net’s products are more “official” than any other. Indeed, when users arrive at C-Net sites after requesting similarly-named better-known competitors, C-Net’s offerings are exactly not the official products users specifically requested by name.

Some C-Net sites are also deceptive in that their titles and graphic design falsely suggest they are an official part of Windows. Consider antispyware.com. The site’s heading presents the generic title “AntiSpyware For Windows” — without mentioning any company name or showing any other prominent indication that the product is not actually part of Windows. Furthermore, antispyware.com shares numerous graphic design elements with official Microsoft sites: Like official Microsoft sites, antispyware.com features a broad blue bar across the top of the page, bold white type at top-left with smaller white type at top-right, a grey navigation bar down the left edge (with thin black lines as section separators, and with simple black text), a grey nav bar down the right edge (with broad grey bars to separate sections, and with blue bulleted text), a grey background, a skewed 3D rendering of a product screen at page center, and a vivid colored bubble at top-center, linking to a product download. See the two screenshots below — antispyware.com on the left, and the official Microsoft Windows Defender download page on the right. These many visual similarities make it especially likely that a user at antispyware.com will mistakenly believe the site is an official Microsoft offering.

 
C-NetMedia’s Antispyware.com
 
Microsoft Windows Defender

Some C-NetMedia sites give users the false impression that they are bona fide informational sites rather than commercial advertisements. For example, Remover.org presents itself as a general-purpose spyware information site, but Remover.org actually promotes only one product — C-Net’s “AntiSpyware For Windows.” Furthermore, Remover.org claims to have “one goal and one purpose: to win the war on spyware” — suggesting a non-commercial purpose, when in fact Remover charges a fee for its removal program. The totality of these practices suggests that a user at Remover.org may reasonably think he is viewing an ordinary informational site and/or a source of unbiased reviews, when in fact the site is a C-Net advertisement.

Hindering Consumer Investigations through Use of Numerous Product Names and Domains

C-Net uses exceptionally many product names and domain names. My analysis indicates that the following products and domains all come from C-NetMedia:

Site Whois IP Address Trademark
adware.pro Whois-Proxy 72.32.100.197  
ad-warealert.com Domains By Proxy (GoDaddy) 72.32.242.170 – C-Netmedia 77047467 – November 20, 2006 – C-Netmedia
adwarealert.com Domains By Proxy (GoDaddy) 72.32.29.230 77047467 – November 20, 2006 – C-Netmedia
adwarearrest.com Syber Corporation
8400 East Prencitce Avenue, Ste 1500  
Greenwood Village CO 80111
72.32.134.197  
adwarebot.com Domains By Proxy (GoDaddy) 72.32.242.171 – C-Netmedia  
antispyware.com Domains By Proxy (GoDaddy) 72.32.26.195 77073855 – December 30, 2006 – C-Netmedia
antispywarebot.com    Domains By Proxy (GoDaddy) 72.32.48.186 77047469 – November 20, 2006 – C-Netmedia
errorkiller.com C&C Networks
3630 County Ct S
Mobile, AL 36619  
72.32.242.171 – C-Netmedia    77047443 – November 20, 2006 – C-Netmedia   
errorsmart.com Domains By Proxy (GoDaddy) 73.32.26.195  
errorsweeper.com Domains By Proxy (GoDaddy) 73.32.48.186 77047440 – November 19, 2006 – C-Netmedia
evidenceeraser.com  Domains By Proxy (GoDaddy) 73.32.29.230 77073969 – December 31, 2006 – C-Netmedia
free-pc-repair.com Ofer Shoshani
747 Durshire Way
Sunnyvale, CA 94087
72.32.100.197  
free-registrysmart.com    Domains By Proxy (GoDaddy) 72.32.242.171 – C-Netmedia 77047441 – November 20, 2006 – C-Netmedia
macrovirus.com Domains By Proxy (GoDaddy) 72.32.242.171 – C-Netmedia  
malwarebot.com Domains By Proxy (GoDaddy) 72.32.242.169 – C-Netmedia 77047470 – November 20, 2006 – C-Netmedia
privacycontrol.com Domains By Proxy (GoDaddy) 73.32.48.186 77073857 – December 31, 2006 – C-Netmedia
privacycontrols.com Domains By Proxy (GoDaddy) 73.32.48.186 77073859 – December 31, 2006 – C-Netmedia
regclean.com Domains By Proxy (GoDaddy) 73.32.48.186  
regrecall.com Domains By Proxy (GoDaddy) 73.32.90.213  
registrybot.com Domains By Proxy (GoDaddy) 72.32.242.169 – C-Netmedia 77047445 – November 20, 2006 – C-Netmedia
registryclear.com Bruce Cope
3630 County Ct S
Mobile, AL 36619
72.32.134.197  
registrysmart.com PrivacyPost (Dotster) 73.32.29.230 77047441 – November 20, 2006 – C-Netmedia
regsweep.com Domains By Proxy (GoDaddy) 73.32.26.195 77047438 – November 19, 2006 – C-Netmedia
remover.org Domains By Proxy (GoDaddy) 72.32.26.195  
restore-pc.com Domains By Proxy (GoDaddy) 73.32.29.230  
spywarebot.com Domains By Proxy (GoDaddy) 73.32.134.197  
spywareremover.com C&C Networks
3630 County Ct S
Mobile, AL 36619
64.49.219.215  

The United States Patent and Trademark Office’s Trademark Search provides the brunt of my evidence that the listed sites are associated with C-Netmedia. Other evidence comes from the 73.32.242.168-175 network block that C-Net uses at Rackspace. (Rackspace also hosts all of the other listed C-Net sites. The 64.49.219.215 server is indeed a Rackspace server, despite its distant IP address.) My conclusion is bolstered by the many other similarities among these sites, including their common substantive theme, structure, layout, registration method, and advertising relationships and suppliers. Furthermore, the sites’ programs are largely similar — with identical detections, false-positives, and user interfaces.

An ordinary user would face substantial difficulty in determining that a given site is operated by C-NetMedia or in finding C-Net’s contact information. At a few of the sites, a user would at least find a street address in Whois. But the other domains all lack useful Whois data. Furthermore, while the listed web sites offer email and/or chat support, they all lack a phone number, mailing address, or even a legal name or place of incorporation. A user seeking to send a formal complaint therefore has no clear means to do so. Savvy users might notice a reference to C-NetMedia within a program’s license agreement. But these references appear only in the licenses shown by programs’ installers — not in the license agreements linked from the corresponding web sites. So these references to C-Net are especially hard to find after a user has already received C-Net software.

A user who manages to identify the C-Net company name, e.g. from trademark applications, is still substantially stymied in learning more about the company. The name “C-NetMedia” immediately suggests an association with CNET Networks, Inc., the well-known news site at www.cnet.com. In fact C-NetMedia and CNET Networks are entirely unrelated. But by choosing a name that matches an existing company, C-Net hinders attempts to learn more about its practices: Searches for “C-Net” overwhelmingly yield references to CNET Networks.

C-Net’s use of many names brings valuable benefits to C-Net but real costs to users: The numerous names prevent users’ unfavorable views of specific C-Net products (examples: 1, 2, 3, 4, 5) from easily spreading to other C-Net products. If C-Net had only a single product, users searching for that product would easily find the complaints of prior dissatisfied users. But by shifting from name to name, C-Net can abandon product names with unfavorable coverage, in each instance starting fresh with a new name. In this regard, C-Net’s approach is strikingly similar to Direct Revenue’s use of dozens of company and product names.

It seems C-Net sometimes uses the name 2squared to describe its offerings. The 2squared.com site claims to be the maker of at least some of C-Net’s products (including ErrorSweeper and RegClean). While C-Net’s trademark applications list one address in Mobile, Alabama (590 B Schillinger Road South, Suite 8), 2squared provides the adjacent suite 10.

C-Net’s trademark applications all list Erik Mv. Pelton as their attorney of record. Mr. Pelton’s tm4smallbiz.com site indicates that he is a bona fide trademark attorney with an office in Arlington, Virginia.

High-Pressure Sales Tactics and False Positives

C-NetMedia SpywareBot False Positives C-NetMedia SpywareBot False Positives

Once a user installs C-NetMedia’s free trial software, C-Net resorts to high-pressure tactics to encourage users to make a purchase.

I tested C-Net’s SpywareBot on a clean PC running Windows XP with no service packs,. My test PC was supplemented only by the ordinary analysis tools I use to study spyware and adware infections. SpywareBot detected Regsnap, my registry change-tracking tool, as the “Absolute Keylogger.” Bold red “Warning” messages repeatedly alerted me to the supposed “43 parasites” on my computer, and a “toast”-style slider arose from the bottom-right corner of my screen. Perhaps this was just an ordinary false positive — a mistake that any security program can make. But C-Net’s error was unusually self-serving in that C-Net requires users to pay a fee — in this case $19.95 — before removing any of the items it detects.

C-Net’s many products mean extended further investigation would be required to fully determine the effectiveness and error rates of C-Net’s various programs. Due to the seriousness of the advertising practices described above, I have chosen to post this article without fully testing for such false positives or other deficiencies across all of C-Net’s programs and across a variety of test computers. I will update this article to link to any such research performed by others.

Other Anomalous Marketing Practices: Affiliate Programs, Certifications, and Logos

C-NetMedia’s marketing programs are striking in their generosity: C-Net offers its affiliates 70% commissions on users’ purchases. Such large commissions tend to suggest that charges to users bear little relationship to the underlying cost of providing the service. In particular, when a user arrives at C-Net’s site through an affiliate link, at least 70% of the user’s payment goes towards marketing costs. But if marketing receives 70% of revenue, relatively little remains to fund product design or other core business functions. A user might be better off with a free product — such as the free products with names nearly identical to the names C-Net selected.

Many C-Net sites feature McAfee Hacker Safe certifications.C-NetMedia sites systematically and prominently tout certifications that are substantially irrelevant to the true attributes of C-Net software. For example, C-Net’s Adwarealert site boasts a McAfee HackerSafe logo. When this logo appears on a site offering security software, a user might reasonably think the logo means the site’s software will keep the user safe from hackers. But in fact HackerSafe signifies nothing of the kind: HackerSafe has merely checked the Adwarealert web server for a set of known security problems. C-Net’s use of the HackerSafe certification thus has the tendency to deceive, i.e. to leave users with an untrue impression of the certification’s significance.

Update (February 14, 11:30am): I notice that McAfee has withdrawn HackerSafe certification of C-NetMedia sites. C-NetMedia sites now show blank space where the logo previously appeared.

Adwarealert also features a Microsoft “Certified for Windows Vista” seal. Microsoft’s certification list confirms that Adwarealert did receive this certification. But it seems Adwarealert does not truly qualify for this certification because Adwarealert violates rule 1.11 of the Microsoft certification requirements, namely the requirement that a certified program comply with all applicable guidelines from the Anti-Spyware Coalition. The ASC’s Risk Model negatively characterizes incomplete or inaccurate identifying information; obfuscation; and misleading, confusing deceptive or coercive messaging or false claims to induce users to take action. By failing to readily provide accurate contact information, by using misleading product names, and by reporting false positives with a request for payment, Adwarealert violates each of these requirements. I therefore conclude that Adwarealert is ineligible for the “Certified for Windows Vista” certification.

C-NetMedia’s sites also feature unsubstantiated claims of product benefits. C-Net sites feature the following logos: “Guaranteed – 100% No Adware or Spyware”, “#1 Most Advanced Privacy Software”, “#1 Registry Cleaner”, “100% Safe and Secure”, “Total Privacy Protection,” “Most Advanced Anti-Spyware Detection,” and “World’s #1 Spyware Remover.” None of these claims contains, references, or links to any substantiation, documentation, or other supporting details. Some of these claims are presented in graphical form, i.e. in logos that appear to be endorsements or certifications. But C-Net gives no indication of any bona fide third party offering these endorsements; instead, the graphics seem to be C-Net’s own creation.


Work To Be Done

My analysis shows ample room for online advertising and security vendors to better protect users from C-NetMedia’s deceptive advertising practices:

  • Google and other search engines could block the widespread deceptive ads from C-NetMedia and its marketing partners. C-Net and its partners have continued these practices for more than a year. Google claims to be tough on malware, and Google does exclude some harmful organic search results. But Google has been ineffective in removing the false and deceptive ads shown above, among many others, despite ample complaints from users and security researchers.
     
  • McAfee could remove its Hacker Safe certification from C-NetMedia sites. At present, the McAfee logo gives users the false impression that McAfee endorses C-Net and the McAfee vouches for the effectiveness of C-Net’s software. I gather neither is truly the case. Indeed, McAfee’s HackerSafe certifies some C-Net sites at the same time that McAfee’s SiteAdvisor characterizes rates those same sites as red. In my view, the SiteAdvisor rating better describes the view of security experts and better serves typical users. (Disclosure: I serve as a member of the Board of Advisors of McAfee SiteAdvisor.) (Update, February 14, 11:30am: McAfee has withdrawn HackerSafe certification of C-NetMedia sites.)
     
  • Microsoft could withdraw its Certified for Windows Vista certification on the basis of C-NetMedia’s violations of various ASC rules, as cited above. Anticipating this kind of harmful marketing practices, Microsoft’s certification rules provide ample basis for excluding C-Net on the basis of its deceptive advertising. Microsoft’s concern should be particularly acute because C-Net copied the layout and format of the Microsoft Antispyware site, because C-Net marketing partners trade on Microsoft’s brand name and product names, and because C-Net products worsen the experience of Windows users (i.e. by charging a fee for security software, when Microsoft provides similar software for free).
     
  • ClickBank could eject C-NetMedia from ClickBank’s affiliate network due to the pattern and practice of false and misleading ads placed by ClickBank affiliates in their promotion of C-Net offers. ClickBank’s Client Contract specifically prohibits fraudulent, deceptive, false or misleading information in advertising messages (clause 7.n.), and Clickbank reserves the right to immediately suspend violators (9.d.). But at present, C-NetMedia seems to remain a ClickBank clent in good standing.

Thanks to security researcher Janie Whitty for references on C-NetMedia’s trademark registrations.

Sears Exposes Customer Purchase History in Violation of Its Privacy Policy

Want to know what a given customer has purchased from Sears? It’s surprisingly easy to find out. Here’s the procedure:

1) Go to the Sears “Manage My Home” site, www.managemyhome.com . Create an account and sign in. Screenshot.

2) On the Home menu, choose Home Profile. In the Search Purchase History section, choose Find Your Products. Screenshot.

3) Enter the name, phone number, and street address of the customer whose purchases you wish to view. Press Find Products. Screenshot.

Sears then displays all purchases its database associates with the specific customer — typically major appliances and other large purchases. See examples from Washington, DC, Brookline, Massachusetts, and Lincoln, Massachusetts.

The look-up form. Full form requires first name, last name, phone number, and address, but nothing more.
    
The purchase listing.  Typically provides specific product, purchase date, warranty, and manuals.
The information required to retrieve a customer’s purchase history   A customer’s purchase history – showing specific items and purchase dates

Sears Fails to Protect Customer Information

Sears offers no security whatsoever to prevent a ManageMyHome user from retrieving another person’s purchase history by entering that person’s name, phone number, and address.

To verify a user’s identity, Sears could require information known only to the customer who actually made the prior purchase. For example, Sears could require a code printed on the customer’s receipt, a loyalty card number, the date of purchase, or a portion of the user’s credit card number. But Sears does nothing of the kind. Instead, Sears only requests name, phone number, and address — all information available in any White Pages phone book.

Neither does Sears even include any special instructions or obligations in its signup agreement with users: The ManageMyHome Terms of Use say nothing about what information users may access. Indeed, while Sears includes a small-type link to its Terms of Use, Sears never asks users to affirmatively accept the Terms.

These Disclosures Are Contrary to Sears’s Explicit Promises

Sears violates its privacy policy when it discloses users’ purchases to the general public. The Sears Customer Information Privacy Policy lists specific circumstances in which Sears may share customer information. These circumstances are relatively broad — allowing Sears to share customer data “with members of the Sears family of businesses … to provide … promotional offers that we believe will be of interest.” Disclosures are also permitted “to provide [users] with products or services that [they] have requested,” to “trusted service providers that need access to your information to provide operational or other support services,” to credit bureaus, and to regulatory authorities and law enforcement. But none of these provisions grants Sears the right to share users’ purchases with the general public.

Sears may argue that its web site privacy policy only applies to users’ online purchases, and does not govern purchases made in retail stores. Perhaps. But I doubt in-store customers expect their friends, neighbors, and the general public to be able to find out what they bought. I’m still trying to determine what privacy (if any) Sears promises its in-store customers.

Sears’s Privacy Breach in Context

Sears’s exposure of customer purchase history fits within a long history of unintended web site disclosures. For example, in October 2000 I showed that Buy.com’s return system was revealing customer names, addresses, and phone numbers at publicly-available URLs. But Sears’s disclosure is more troubling: Sears discloses the specific products users purchased. Sears’s disclosures apply to all users, not just those who return products. And Sears’s disclosures come some 7+ years after Buy.com’s breach — a period of great advance in online security.

The combination of data Sears provides could open the door to serious harms to Sears customers. ManageMyHome reports the specific products customers purchased, as well as the dates of each such purchase. With this information, a miscreant could approach a customer and pretend to be a Sears representative. Consider: “Your washing machine was recalled, and I need to install a new motor.” Or, “I’m here to provide the free one-year check-up on your dishwasher.”

Assessing Sears’s IT Strategy

The ManageMyHome site offers some useful services: Consolidated information about dates of purchase, clear listing of warranty status, and easy links to product manuals. Sears touted these benefits in its recent coverage of ManageMyHome.

But as soon as Sears resolved to provide online access to customers’ purchase histories, Sears staff should have recognized the need to determine which users are truly authorized to see this information. Sears’s failure to effecitvely authenticate users is therefore puzzling. Did Sears staff fail to notice the problem? Decide to ignore it when they couldn’t devise an easy solution to protect users’ purchase histories? Resolve to argue that purchase history merits no better protection than the current system provides?

Combining this privacy breach with Sears’s poorly-disclosed installation of ComScore tracking software, it appears that Sears is not effectively protecting its users’ and customers’ privacy. Perhaps that’s no surprise in light of Sears’s recent financial distress — a 99% drop in profits in third quarter 2007, compared with the third quarter of 2006. But users need not accept excuses for Sears’s lackadaisical treatment of their private information. No matter the company’s financial standing, Sears ought to comply with its stated privacy policy and treat user information with the care users rightly expect.

Sears’s Response

I wrote to Sears ManageMyHome via the addresses on their Contact Us page. To their credit, they responded quickly (less than ninety minutes). However, their reply does not address the seriousness of this situation. Their reply follows:

“We appreciate that you have a security concern. Thank you for taking the time to share your comments with us. We appreciate hearing feedback from our customers, and will pass this information to the appropriate area to research.”

Update (January 4, 5pm): Sears has disabled the search feature described above. Attempts to retrieve a purchase history now yield the message “We’re sorry, this feature is currently disabled.”

Thanks to an anonymous contributor, using pseudonym Heather H, for the tip that led to this article.

The Sears "Community" Installation of ComScore

Late last month, Benjamin Googins (a senior researcher in the Anti-Spyware unit at Computer Associates) critiqued a ComScore installation performed by Sears’ “Sears Holdings Community” (“My SHC Community” or “SHC”). After reviewing the installation sequence, Ben concluded that the installation offered “very little mention of software or tracking” and otherwise fell short of CA and industry standards. I agree.

I write today to add my own critique. I begin by presenting the entire installation sequence in screenshots and video. I then explain why the limited notice provided falls far short of the standards the FTC has established. Finally, I show that Sears’ claims of adequate notice are demonstrably false.

The SHC Installation Sequence

The SHC installation proceeds in four steps:

1) An email from Sears after a user provides an address at Sears.com. In seven paragraphs plus a set of bullet points, 582 words in total, the email describes the SHC service in general terms. But the paragraphs’ topic sentences make no mention of any downloadable software, nor do the bullet points offer even a general description of what the software does. The only disclosure of the software’s effects comes midway through the fourth paragraph, where the program is described as “research software [that] will confidentially track your online browsing.” Sophisticated users who notice this text will probably abandon installation and proceed no further. But novices may mistakenly think the tracking is specific to Sears sites: SHC is a research program offered by Sears, so it is difficult to understand why tracking would occur elsewhere. Furthermore, the quoted text appears midway through a paragraph — in no way brought to users’ attention via topic sentences, headings, section formatting, or other labels. So it’s strikingly easy to miss.

2) If a user presses the “Join” button in the email, the user is taken to a SHC web-based installation sequence that further details SHC’s offerings. The first page describes some aspects of SHC in reasonable detail — with six prominent and clear bullet points. Yet nowhere does this text make any mention whatsoever of downloadable software, market research, or other tracking.

3) Pressing “Join” in the SHC screen takes a user to a “Welcome to My SHC Community” page which requests the user’s name, address, and household size. The page then presents a document labeled “Privacy Statement and User License Agreement” — 2,971 words of text, shown in a small scroll box with just ten lines visible, requiring fully 54 on-screen pages to view in full. The initial screen of text is consistent with the “privacy statement” heading: The visible text indicates that the document describes “what information [SHC] gather[s and] how [SHC] use[s] it” — typical subjects for a privacy policy. But despite the title and the first screen of text, the document actually proceeds to an entirely different subject, namely downloadable software and its far-reaching effects: The tenth page admits that the application “monitors all of the Internet behavior that occurs on the computer on which you install the application, including … filling a shopping basket, completing an application form, or checking your … personal financial or health information.” That’s remarkably comprehensive tracking — but mentioned in a disclosure few users are likely to find, since few users will read through to page 10 of the license.

    Within the Privacy Statement section, a link labeled “Printable version” offers users a full-screen version of the document, requiring “only” ten on-screen pages on my test PC. But nothing in the Privacy Statement caption or visible text suggests that the document merits such thorough review. Due to the labeling and the first screen of text, few users will see any need to click through to the full-screen version.

4) A user next arrives at a screen labeled “You’re almost finished!” Clicking “Next” triggers an ActiveX screen offering an unnamed program, signed by a company called TMRG, Inc. (nowhere previously mentioned in the installation sequence), authenticated by Thawte (part of VeriSign). Pressing Yes in the ActiveX yields an installation program with no further opportunity to cancel installation. Packet sniffer analysis confirms that ComScore software is installed.

See also a video of the installation sequence.

Relevant FTC Rules

The FTC’s recent settlements with Direct Revenue and Zango explain the disclosure and consent required before installing tracking software on users’ computers. To install such software on users’ PCs, vendors must obtain “express consent” — defined to require “clear[] and prominent[] disclos[ure of] the material terms of such software … including the nature and purpose of the program and the effects it will have … prior to the display of, and separate from, any final End User License Agreement.” “Clear[] and prominent[]” installations are defined to be those that are “unavoidable”, among other requirements.

The Sears SHC installation of ComScore falls far short of these rules. The limited SHC disclosure provided by email lacks the required specificity as to the nature, purpose, and effects of the ComScore software. Nor is that disclosure “unavoidable,” in that the key text appears midway through a paragraph, without a heading or even a topic sentence to alert users to the important (albeit vague) information that follows.

The disclosure provided within the Privacy Statement and User License Agreement also cannot satisfy the FTC’s requirements. The FTC demands a disclosure “prior to … and separate from” any license agreement, whereas the only disclosure on this page occurs within the license agreement — exactly contrary to FTC instructions. Furthermore, users can easiliy overlook text on page ten of a lengthy license agreement. Such text is the opposite of “unavoidable.”

The SHC/ComScore violation could hardly be simpler. The FTC requires that software makers and distributors provide clear, prominent, unavoidable notice of the key terms. SHC’s installation of ComScore did nothing of the kind.

Other Installation Deficiencies

Beyond the problems set out above, the SHC installation also falls short in other important respects.

Failure to provide the promised additional information. Sears’ initial email promises that “during the registration process, you’ll learn more about this application software.” In fact, no such information is provided in the visible, on-screen installation sequence. Based on this false promise and users’ general experience, users may reasonably expect that the download link in step 4 will offer additional information about the software at issue, along with an opportunity to cancel installation if desired. In fact no such information is ever provided, nor do users have any such opportunity to cancel.

Choosing little-known product names that prevent users from learning more. The initial SHC email refers to the ComScore software as “VoiceFive.” The license agreement refers to the ComScore software as “our application” and “this application” without ever providing the application’s name. The ActiveX prompt gives no product name, and it reports company name “TMRG, Inc.” These conflicting names prevent users from figuring out what software they are asked to accept. Furthermore, none of these names gives users any easy way to determine what the software is or what it does. In contrast, if SHC used the company name “ComScore” or the product name “RelevantKnowledge,” users could run a search at any search engine. These confusing name-changes fit the trend among spyware vendors: Consider Direct Revenue’s dozens of names (AmazingMerchants, BestDeals, Coolshopping, IPInsight, Blackone Data, Tps108, VX2, etc.).

Critiquing Sears SHC’s Response

To my surprise, Sears defends the practices described above. In a reply to CA’s Ben Googins, Sears SHC VP Rob Harles claims that SHC “goes to great lengths to describe the tracking aspect.” In particular, Harles says “[c]lear notice appears in the invitation”, “on the first signup page”, and “in the privacy policy and user licensing agreement.”

I emphatically disagree. The email invitation provides vague notice midway through a lengthy paragraph that, according to its topic sentence, is otherwise about another topic. The first signup page makes no mention at all of any downloadable software. The privacy policy and license agreement describe the software only in the tenth page of text (where few users are likely to find the disclosures), and even then it fails to reference the program by name.

Harles further claims that the installer provides “a progress bar that they [users] can abort.” Again, I disagree. The video and screenshots are unambiguous: The SHC installer shows no progress bar and offers no abort button.

The Installation in Context

In June 2007, I showed other examples of ComScore software installing without consent — including multiple installations through security exploits. TRUSTe responded by removing ComScore’s RelevantKnowledge from TRUSTe’s Trusted Download Program for three months. Now that more than five months have elapsed, I expect that ComScore is seeking readmission. But the installation shown above stands in stark contrast to TRUSTe Trusted Download rules. See especially the requirement that primary notice be “clear, prominent and unavoidable” (Schedule A, sections 3.(a).(iii) and 1.(hh)).

Why so many problems for ComScore? The basic challenge is that users don’t want ComScore software. ComScore offers users nothing sufficiently valuable to compensate them for the serious privacy invasion ComScore’s software entails. There’s no good reason why users should share such detailed information about their browsing, purchasing, and other online activities. So time and time again, ComScore and its partners resort to trickery (or worse) to get their software onto users’ PCs.