Wildfire makes a variety of white-label cashback browser extensions. Some of their extensions—including at least Acorns, KashKick, and Super.com — open messages inviting user to “reactivate” cashback after another affiliate has claimed credit, even though affiliate network rules require the extensions to stand down in those circumstances.
Here’s the sequence. First, a user installs a Wildfire partner shopping extension. When a user browses a merchant site, the extension pops open a window inviting the user to click and earn cashback. Suppose the user later clicks an affiliate link from another publisher to the same merchant. Wildfire then pops open a “reactivate” window encouraging the user to click the Wildfire offer again—thereby replacing the other publisher’s attribution with Wildfire’s.
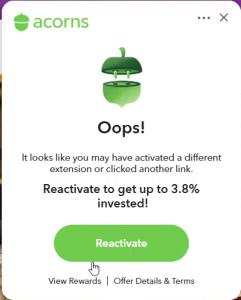
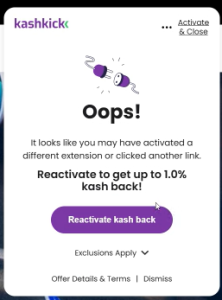
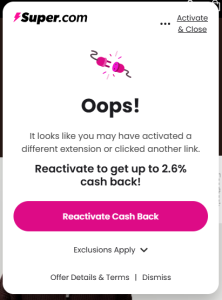
See also this WildFire Acorns video showing me browsing Zulily, receiving and clicking a Wildfire Acorns popup, then browsing Retailmenot, clicking back to Zulily, and receiving the Acorns “reactivate” popup. All testing by me, on a test device, September 28, 2026 in my lab.
Network rules
Affiliate network rules disallow Wildfire’s “reactivate” window. Consider the leading US affiliate networks
CJ’s Publisher Service Agreement prohibits software publishers from “usurp[ing] a Transaction that might otherwise result in a Payout to another Publisher.” Wildfire’s reactivate window claims funds that “might otherwise” flow to another publisher.
Impact’s Stand-Down Policy requires publishers to “refrain from actions that could … interfere with existing publisher-referred traffic.” Impact continues: “Upon detecting prior publisher attribution, software must suppress marketing prompts: Do not display pop-ups, banners, or notifications encouraging users to activate cashback or other affiliate offers.” Wildfire’s reactivate window “encourag[es]” a user to activate cashback.
Rakuten’s Network Policies explain that “’Stand-down’ means the software may not activate or redirect the end user to the advertiser site with their Supplier Affiliate link for the duration of the browser session.” Wildfire’s reactivate window is a form of extension “activat[ion]” prohibited by that sentence.
Wildfire’s role
Because Wildfire supplies the underlying technology for multiple white-label extensions, the same design can affect multiple publishers and merchants. My technical analysis, below, indicates that the stand-down/reactivation functionality resides in Wildfire’s shared code rather than being separately implemented by each white-label extension.
Implementation details
Reviewing Wildfire’s code within the Acorns extension, I found that the reactivate function has a featureFlag setting. From src/shared/config.js:
featureFlags: { lostAffiliationDetectionEnabled: true }
I also reviewed the Wildfire code that consumes this setting and decides how to proceed. First, handleAffiliateStandDown.js watches web requests. If a request’s query string contains a parameter from the LostAttribution list in _standDownPolicy, it sets potentialLossOfAttributionDetectedFromTab. Later, handleLostAttribution.js runs when the tab finishes loading. It checks that cashback was already activated for that domain and that the URL differs from the original activation URL. It then sends a LOST_ATTRIBUTION message to the tab, prompting the reactivate message as shown above.
The code indicates that the lost-attribution/reactivation feature resides in Wildfire’s shared code, rather than being separately implemented by the individual shopping extensions. That is consistent with remarks on Wildfire’s site (“white-label”).
Remediation
In the telemetry sent from the user’s device to Wildfire’s server, Wildfire tracks the fact that another affiliate’s link was clicked (“LOST_AFF” in yellow below), but also the specific other affiliate that was to be credited (usually visible in the merchant’s landing page, url= parameter, in green below — here RetailMeNot with Rakuten publisher ID OOTtr9mlaCk).
GET https://wild.link/_sales/offer-view?d=51138069&c=4782751
&sc=&tc=696f885f-40ef-4cc1-aacb-357784ef9a6b&session_id=
b41104b1-8a3a-4b2f-abb4-03941e3c255f&session_step=1
&url=https%3A%2F%2Fwww.zulily.com%2F%3Futm_source%3DAffiliate
%26utm_medium%3Daffiliate%26utm_content%3DRetailMeNot
%26ranMID%3D54167%26ranEAID%3DOOTtr9mlaCk%26ranSiteID%3D
OOTtr9mlaCk-CHIdllrXwa1nTnnT5TSbWw&view=LOST_AFF
&action=OFFER_VIEWED&app_version=11.11.1 HTTP/1.1
This data creates a path to return funds to the publishers who would have been paid had it not been for Wildfire’s reactivate messages. Any payment Wildfire and its partners received in a LOST_AFF session could then be identified for review and, where appropriate, redirected or reimbursed to the affected affiliate (per the green url= parameter).
Full remediation would also require Wildfire paying networks’ costs of investigating the violation.